ActionTuner
Find risky GitHub Actions permissions, unpinned dependencies, and exposed secrets across repositories, then deliver prioritized fixes for lean engineering teams.
What is ActionTuner?
ActionTuner is a proposed GitHub Actions security scanner for lean engineering teams. It would examine repositories for risky workflow permissions, unpinned third-party actions, and exposed secrets, then turn its findings into a prioritized, actionable remediation plan.
The idea addresses a practical problem: continuous integration and continuous delivery (CI/CD) workflows are software, but they are not always reviewed with the same security rigor as application code. A workflow can run with broad permissions, execute code from an external action, or handle a credential in an unsafe way. Any of these weaknesses can give an attacker a path to modify code, access secrets, or disrupt a release.
The product opportunity is not simply to produce another security report. ActionTuner’s value would come from helping a small team understand which GitHub Actions risks matter most, why they matter, and how to fix them without slowing down development.
In one sentence: ActionTuner would help teams find and fix GitHub Actions security risks across repositories, with prioritization designed for teams that do not have a dedicated application security department.
Why GitHub Actions security is a meaningful problem
GitHub Actions makes it possible to automate builds, tests, deployments, and other development tasks using workflow files stored in a repository. That convenience also makes workflow configuration a part of the software supply chain. A workflow may run code, use third-party actions, receive tokens, and interact with cloud infrastructure.
A security issue in an application can be serious. A security issue in a workflow can also affect the process used to build, test, or publish that application. This means workflow security is not an isolated configuration concern; it is part of protecting the systems and credentials that support software delivery.
GitHub’s official guidance on security hardening for GitHub Actions discusses risks and mitigations that teams should consider. ActionTuner could help operationalize that guidance by checking repositories continuously and translating relevant findings into a manageable backlog.
Common areas to assess include:
- Workflow permissions: Whether a workflow or job has more access than it needs.
- Third-party actions: Whether actions are referenced in a way that can change unexpectedly.
- Secrets handling: Whether credentials are exposed through workflow configuration or unsafe execution patterns.
- Untrusted input: Whether user-controlled data can influence commands or scripts.
- Repository coverage: Whether a team has a consistent view of risk across all its repositories.
- Remediation ownership: Whether a finding has a clear owner, explanation, and next step.
The challenge for smaller teams is often not a lack of security guidance. It is the work required to apply that guidance consistently across repositories and keep doing so as workflows change.
Target audience for ActionTuner
ActionTuner should begin with teams that use GitHub Actions regularly but have limited capacity to review workflow security by hand. A narrow initial audience would make the product easier to validate than a broad promise to serve every organization with a GitHub account.
Primary customers
Lean engineering teams at growing software companies are a strong initial segment. They may have a handful of engineers or several product squads, a growing number of repositories, and a release process that depends on automated workflows. These teams need understandable security feedback without the operational overhead of a large security platform.
Other promising customer groups include:
- Startups preparing for enterprise sales: They may need to demonstrate security practices to customers but lack a large security team.
- Developer platform teams: They manage shared workflows or reusable actions and need to identify configuration drift across repositories.
- Small security teams: They want a focused way to find and triage GitHub Actions risks without building custom scripts.
- Open-source maintainers: They may want to improve the security posture of public repositories, although their willingness to pay could differ from commercial teams.
- Consultancies and managed service providers: They may need repeatable workflow reviews across multiple client organizations.
Jobs customers need to get done
A successful product should address practical jobs rather than selling a vague promise of “better security.” For example, a customer may need to:
- See which repositories have the most urgent workflow risks.
- Understand why a specific permission or dependency is risky.
- Know whether a finding can be safely fixed automatically.
- Track whether a fix has been applied and verified.
- Explain the team’s remediation process to a customer, auditor, or internal stakeholder.
These jobs suggest that ActionTuner should be built around a finding-to-fix workflow. A scanner that identifies issues but leaves users to interpret, prioritize, and track them will provide less value than a tool that supports the full remediation process.
Likely buyer and daily user
The daily user could be a platform engineer, DevOps engineer, or security-minded developer. The buyer may be an engineering leader or a security lead responsible for improving controls across several repositories.
This distinction matters for product design. Developers need precise, contextual findings inside their normal workflow. Buyers need visibility into coverage, trends, ownership, and remediation progress. A useful product should satisfy both without turning its interface into a dense compliance dashboard.
The market opportunity and product gap
There are established tools for code analysis, dependency monitoring, secret detection, and cloud security. GitHub also provides security capabilities and documentation. ActionTuner would therefore enter a market with existing solutions—not an empty category.
The opportunity is to focus on a specific operational gap: helping lean teams consistently assess and remediate risks in GitHub Actions configuration across repositories. The key question is not whether a security check exists somewhere. It is whether the intended customer can find the relevant risk, understand it, assign it, and fix it with reasonable effort.
A focused GitHub Actions security scanner could differentiate itself through:
- Workflow-specific context: Findings explain the affected workflow, job, permission, action reference, or input pattern.
- Prioritization: The product helps a user distinguish urgent exposure from lower-impact improvements.
- Practical remediation: Recommendations show a concrete change and explain any trade-offs.
- Multi-repository visibility: Teams can see coverage and progress across their organization.
- Developer-friendly delivery: Findings can be presented where teams already work, such as pull requests or issue trackers.
- Low operational burden: Onboarding should not require a lengthy security program or complicated infrastructure.
This gap should be validated through customer interviews and prototype testing. A product team should not assume that every engineering group experiences the same pain or will pay for the same feature set. For example, a startup may value a fast repository scan and a clear fix list, while a platform team may prioritize policy enforcement and organization-wide reporting.
How to validate demand
Before building a broad platform, test the underlying problem with target users. Useful discovery questions include:
- How do you currently review GitHub Actions workflows?
- What types of workflow findings have you encountered recently?
- How do you decide which finding to fix first?
- Who owns workflow security in your organization?
- What happens when a finding spans many repositories?
- Which existing tools do you use, and where do they fall short?
- What evidence would you need before granting a scanner access to your repositories?
- Would you pay for continuous monitoring, a one-time review, or both?
Ask for examples of recent work rather than relying only on general opinions. A participant who can describe a real incident, audit finding, delayed release, or manual review process offers stronger evidence than someone who simply says the product sounds useful.
Core features and solution details
The first version should focus on accurate findings and a credible remediation experience. Adding many checks is not valuable if users cannot trust the results or tell what to do next.
1. Read-only repository connection
ActionTuner should start with a secure, least-privilege connection to GitHub. During setup, the user should understand what data the product reads, why it needs that access, how long results are retained, and how to disconnect the integration.
A read-only MVP is easier to trust than a tool that immediately requests permission to edit workflows. Automated pull requests may become a useful later feature, but users should be able to inspect recommendations before granting write access.
2. Workflow inventory and coverage
Before prioritizing risks, the product needs to know what it has scanned. An inventory can show:
- Repositories connected to the product.
- Workflow files discovered in each repository.
- The last scan time and scan status.
- Repositories that could not be analyzed.
- Findings grouped by repository, severity, and category.
Coverage reporting is especially important in multi-repository environments. Without it, a team may mistake an incomplete scan for a clean security posture.
3. Risky permissions analysis
A core capability should identify broad or unnecessary workflow permissions. GitHub Actions permissions can determine what a workflow’s token may access, so teams should aim to grant only the access needed for a job.
ActionTuner should distinguish between a permission that is explicitly required and one that appears broader than necessary. Recommendations should avoid simplistic fixes that break legitimate workflows. For example, reducing permissions may be appropriate, but the product should explain what the workflow needs to do and how a change could affect it.
4. Unpinned third-party actions
A workflow that references an action using a mutable version tag may not receive an immutable dependency reference. Pinning an action to a full commit SHA can make the reference more predictable, although it also creates a maintenance responsibility: teams need a process for reviewing and updating pinned versions.
A useful finding should explain:
- Which workflow references the action.
- How the action is currently referenced.
- Why the current reference may be less predictable.
- What a pinned reference changes.
- How the team can update the pin over time.
ActionTuner should present dependency pinning as a control with a lifecycle, not a one-time checkbox.
5. Secret exposure checks
The product can detect suspicious patterns involving credentials in workflow files and related configuration. It should be careful not to claim that it can detect every exposed secret. A scanner can find known patterns or risky usage, but secret exposure may also occur in logs, external systems, runtime output, or other places outside the scanner’s visibility.
Findings should therefore communicate scope clearly. If ActionTuner only scans workflow configuration, it should say so. It should also avoid storing secret values in scan results. Where possible, the scanner should report the location and type of concern without copying sensitive content into its own database or notifications.
6. Prioritized findings and remediation guidance
A useful finding should answer five questions:
- What did the scanner detect?
- Where did it find the issue?
- Why could it matter?
- How confident is the product in its assessment?
- What is the recommended next step?
Prioritization should account for context rather than relying on a label alone. A broad permission in a workflow that publishes a release may deserve different treatment from a similar configuration in a low-impact test workflow. The initial product may use transparent rules and severity levels rather than promising sophisticated risk prediction.
7. Pull request and issue workflows
Once recommendations are reliable, ActionTuner could help teams move from findings to fixes by:
- Creating issues with repository and workflow context.
- Adding annotations or summaries to pull requests.
- Grouping related findings into remediation tasks.
- Opening suggested pull requests for low-risk changes.
- Re-scanning after a fix and closing resolved findings.
Automatic changes should be introduced cautiously. A product that modifies workflows without clear review can disrupt builds or deployments. Suggested pull requests with human approval are a safer first step than unattended edits.
8. Policies and organization-level reporting
As customers grow, they may want policy controls such as:
- A rule requiring explicit permissions.
- A policy for how external actions are referenced.
- A threshold for high-priority findings.
- A view of unresolved issues by team or repository.
- Evidence showing scan history and remediation status.
These features should follow demonstrated customer demand. For an MVP, a clear repository list and actionable findings may be more valuable than a configurable policy engine.
Competitive advantage and positioning
ActionTuner should avoid positioning itself as a replacement for every security tool a company already uses. A more credible position is a focused GitHub Actions security scanner that complements existing security workflows.
| Product approach | Workflow-specific focus | Multi-repository view | Actionable fixes | Low setup burden | Clear fit for lean teams |
|---|---|---|---|---|---|
| Generic code scanner | Limited | Varies | Varies | Varies | Varies |
| Manual workflow review | High | Often limited | Depends on reviewer | Low initial setup | Difficult to sustain |
| Custom internal scripts | Varies | Varies | Usually limited | High maintenance | Depends on internal skills |
| ActionTuner concept | High | Core capability | Core capability | Product goal | Core audience |
The table describes positioning hypotheses, not an independently verified feature comparison of specific vendors. Before publishing a competitive comparison on a live website, validate each named competitor’s current capabilities using its official documentation.
The unique selling proposition
The strongest potential USP is prioritized GitHub Actions security remediation designed for lean engineering teams. That differentiates the product through focus and usability rather than by claiming that no other scanner can identify workflow risks.
The advantage could become durable if ActionTuner earns trust through:
- High-quality, low-noise findings.
- Remediation recommendations that preserve working workflows.
- Clear explanations of scan scope and confidence.
- A smooth path from detection to verified resolution.
- Useful organization-level reporting without heavyweight implementation.
Trust is especially important in security software. A scanner that creates false positives, requests excessive access, or obscures how it handles repository data can undermine its own value proposition.
Recommended technology stack
The technology choices should support secure integration, fast iteration, and reliable scanning. The exact stack depends on the founders’ experience and deployment requirements, but the following is a practical starting point.
Product interface and application
A TypeScript-based web application using React can support a dashboard for repository inventory, findings, policies, and remediation status. A framework such as Next.js may be suitable if the team wants routing, server-side capabilities, and a unified application structure.
For styling, Tailwind CSS can help a small team build and iterate on consistent interfaces quickly. The trade-off is that teams need conventions for reusable components and design tokens as the application grows.
Backend and data layer
A conventional API service can manage organization connections, scan jobs, findings, and user permissions. A relational database such as PostgreSQL is a reasonable choice for entities that have clear relationships, including organizations, repositories, workflow files, scans, and findings.
The system should keep sensitive installation credentials and tokens out of ordinary application tables and logs. Use a managed secrets service or a cloud key-management solution, apply encryption in transit and at rest, and define a retention policy for repository content and scan output.
Scan processing
Run scans in separate background workers rather than tying lengthy analysis to a user’s browser session. A job queue can coordinate repository events, scheduled scans, retries, and rate limits. Workers should be isolated from the web application and should receive only the data and permissions required for a particular scan.
A scanner can begin as a deterministic rules engine. That approach is easier to explain, test, and audit than using a language model to make security decisions. Machine learning or generative AI might later help summarize findings, but deterministic checks should remain the basis for detection and policy enforcement.
GitHub integration
Use GitHub’s official documentation as the source of truth for authentication, app permissions, webhook handling, and Actions behavior. Prefer an integration model that grants narrowly scoped access and lets customers choose repositories where possible.
The product should be designed for webhook retries, duplicate events, and rate limits. It should also periodically reconcile repository state, since webhook delivery alone may not provide a complete picture of changes.
Security and observability
Security-sensitive SaaS products need secure engineering practices from the beginning. Useful foundations include:
- Multi-factor authentication support through the identity provider.
- Role-based authorization for organization and repository data.
- Audit logs for account changes and integration activity.
- Rate limits and abuse monitoring.
- Dependency and container scanning for ActionTuner itself.
- Backups, incident response procedures, and tested recovery processes.
- Redaction of tokens, secrets, and sensitive repository content from logs.
For deployment, choose a cloud provider and managed services the founding team can operate responsibly. The best stack is not the one with the most components; it is the one the team can secure, monitor, and maintain.
Monetization strategy options
ActionTuner can test several pricing models, but pricing should reflect the product’s value metric and the buyer’s mental model.
Repository-based subscription
Charge by the number of monitored repositories. This is easy to understand and maps directly to scan coverage. The risk is that customers may avoid adding repositories to control costs, reducing the product’s visibility and value.
Organization-based tiers
Offer plans based on organization size, repository limits, or advanced capabilities. A simple entry tier can support small teams, with higher tiers adding policy controls, audit exports, or centralized reporting.
Usage-based pricing
Charge based on scans or analysis volume. This can align price with operating costs, but unpredictable bills may discourage continuous monitoring. If using this model, provide clear estimates and spending controls.
Free scan with paid monitoring
A free initial scan can demonstrate product value and make evaluation easier. Paid plans can include ongoing scans, remediation tracking, notifications, and organization-level reporting. The free offering must be designed carefully so that it attracts relevant buyers without creating unsustainable support costs.
Security review or managed service add-on
Some teams may want expert help interpreting findings or planning remediation. A one-time review or assisted onboarding service could help validate demand while providing early customer insight. It should not become a substitute for a repeatable SaaS product unless customers demonstrate that services are a lasting requirement.
Early pricing experiments should measure more than sign-ups. Track whether teams connect repositories, return to the product, remediate findings, and agree to pay for continued monitoring.
Risks and mitigation
A security product must address its own security and trust risks as deliberately as the risks it scans.
False positives and alert fatigue
Risk: Noisy findings can cause users to ignore the product.
Mitigation: Start with a small set of high-confidence checks. Show evidence and rationale, allow users to mark findings as accepted or not applicable, and test rules against real workflows before broad release.
False negatives and incomplete coverage
Risk: Users may assume that a clean report means their workflow is fully secure.
Mitigation: State exactly what the scanner checks, show scan coverage and limitations, and avoid absolute claims such as “your workflows are secure.” Expand detection only when the product can explain and test the additional checks.
Excessive integration permissions
Risk: Customers may reject an integration that requests more access than needed.
Mitigation: Request the minimum permissions required, explain each permission in plain language, offer repository selection where supported, and make disconnection and access revocation easy to find.
Handling sensitive code and credentials
Risk: Scanning may expose the product to confidential source code, tokens, or sensitive workflow data.
Mitigation: Minimize collection, avoid persisting full repository content unless necessary, redact sensitive values, encrypt stored data, restrict employee access, and document retention and deletion behavior. Make these practices part of the product design, not just a page in the privacy policy.
Breaking customer workflows
Risk: A recommended change could cause a build, release, or deployment to fail.
Mitigation: Explain the expected impact, provide a suggested diff, encourage human review, and support rescanning after changes. Keep automated pull requests optional until the product has strong evidence that specific changes are safe.
Platform dependency
Risk: The business depends on GitHub APIs and product behavior that may change.
Mitigation: Monitor official platform documentation, build resilient integration handling, and avoid promising functionality that depends on unsupported behavior. A focused GitHub product can still create value, but its roadmap should account for platform changes.
Difficult customer acquisition
Risk: Smaller teams may acknowledge workflow security risks but lack budget or urgency.
Mitigation: Target teams with a clear trigger, such as enterprise security review, a growing repository portfolio, a platform engineering initiative, or a recent workflow-related finding. Test willingness to pay before investing in advanced features.
Competitive pressure
Risk: Existing security platforms may add similar checks.
Mitigation: Compete on workflow-specific usability, remediation quality, transparent coverage, and fast time to value. Build a product customers prefer to use, not a feature checklist that can be copied without understanding the customer workflow.
How to measure product-market fit
ActionTuner should measure whether it helps customers improve security outcomes, not just whether it generates scans.
Useful early metrics include:
- Percentage of connected repositories scanned successfully.
- Time from repository connection to first useful finding.
- Percentage of high-priority findings assigned an owner.
- Median time from finding discovery to verified resolution.
- Repeat usage by engineering and security stakeholders.
- False-positive reports and accepted-risk rates.
- Trial-to-paid conversion and renewal behavior.
- Number of repositories monitored per paying organization.
These metrics need context. A high number of findings may indicate useful detection, but it can also indicate a noisy product. A short time to resolution may be a positive signal, but only if the issue was genuinely fixed and not simply dismissed.
Actionable implementation steps
A disciplined launch plan should validate the problem before expanding the feature set.
Interview target teams
Speak with engineering leaders, platform engineers, security practitioners, and maintainers who use GitHub Actions. Focus on real incidents, review processes, recurring pain, and existing tools. Look for a consistent customer segment with a repeated, expensive problem.
Define a narrow first release
Choose a small set of checks, such as overly broad permissions, mutable action references, and selected secret-handling risks. Write down what each check detects, what it cannot detect, and how a user should remediate it.
Build a read-only prototype
Create the minimum experience needed to connect a repository, scan workflows, display evidence, and explain recommended actions. Avoid automatic edits and broad policy configuration until customers validate the core workflow.
Test against real repositories
With permission, test the scanner on a diverse set of public or customer-approved repositories. Measure detection accuracy, missed cases, scan reliability, and time required for a user to understand a finding. Do not treat synthetic examples as a substitute for real workflow complexity.
Validate the trust model
Review requested permissions, data handling, token storage, logging, retention, deletion, and incident response. Ask prospective customers what would prevent them from installing the product and address those objections explicitly.
Run a paid pilot
Offer a focused pilot with a clear scope and success criteria. Learn whether customers will pay for continuous visibility and remediation, not merely whether they will try a free scanner.
Expand based on evidence
Add pull request workflows, policy management, reporting, and additional checks only when customer behavior shows that these capabilities solve a recurring problem. Keep accuracy and explainability ahead of feature count.
For founders building the product, TurboStarter can help accelerate SaaS development so the team can spend more time validating the product’s security workflow, customer experience, and pricing assumptions.
Final assessment
ActionTuner is a focused SaaS opportunity built around a real engineering concern: GitHub Actions workflows can carry permissions, dependencies, and credentials that deserve ongoing review. The concept is strongest when it serves lean teams that need a practical way to identify and remediate risks across repositories without building a dedicated internal security program.
Its success will depend on trust and execution. The scanner must be accurate enough to earn attention, narrow enough to stay understandable, and careful enough with repository access to meet customer expectations. Prioritized remediation—not simply another list of alerts—should be the product’s defining experience.
The next step is not to build every possible security feature. It is to validate the customer, test a small set of high-confidence checks, and demonstrate that teams will use and pay for a reliable path from workflow finding to verified fix.
More 🏢 B2B Application SaaS ideas
Discover more innovative b2b application SaaS ideas that are trending in 2026. Each idea is AI-generated with market validation and growth potential to help you find your next profitable venture faster than competitors.
Your competitors are building with TurboStarter
Below are some of the SaaS ideas that have been generated and built with our starter kit.
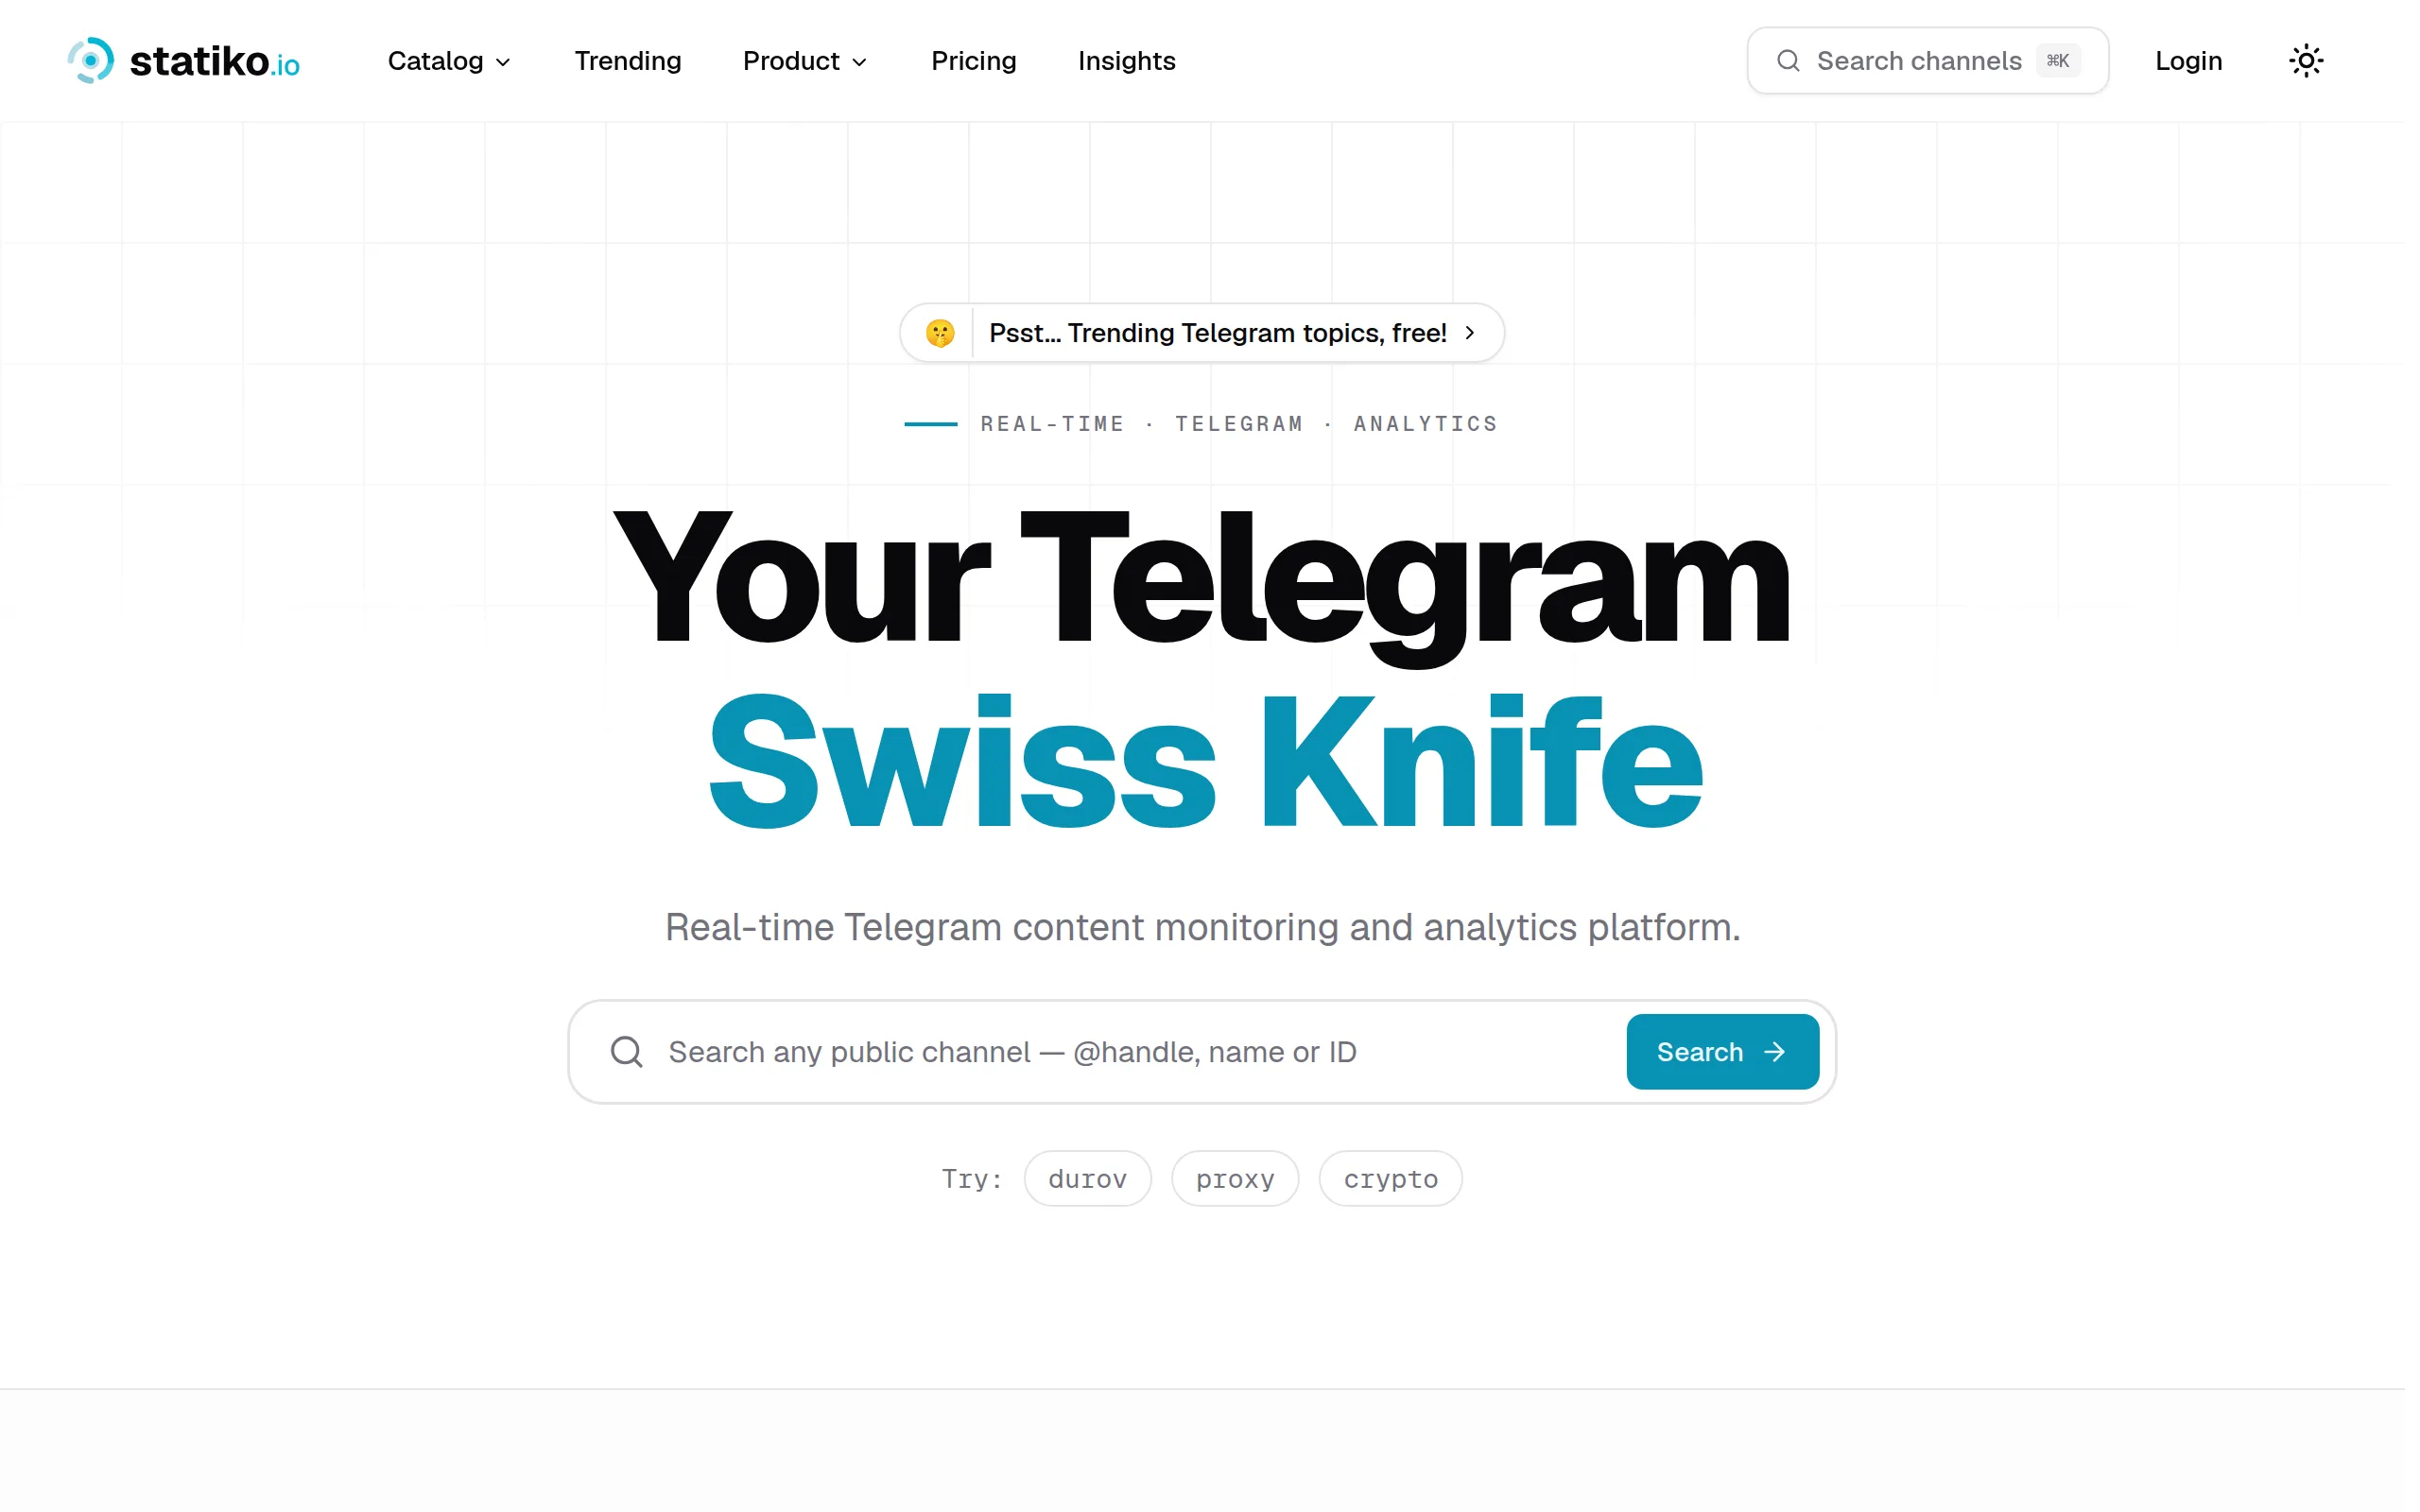
Statiko
Monitor any Telegram channel in real time - track posts, edits, deletions, and growth with AI recaps 📡
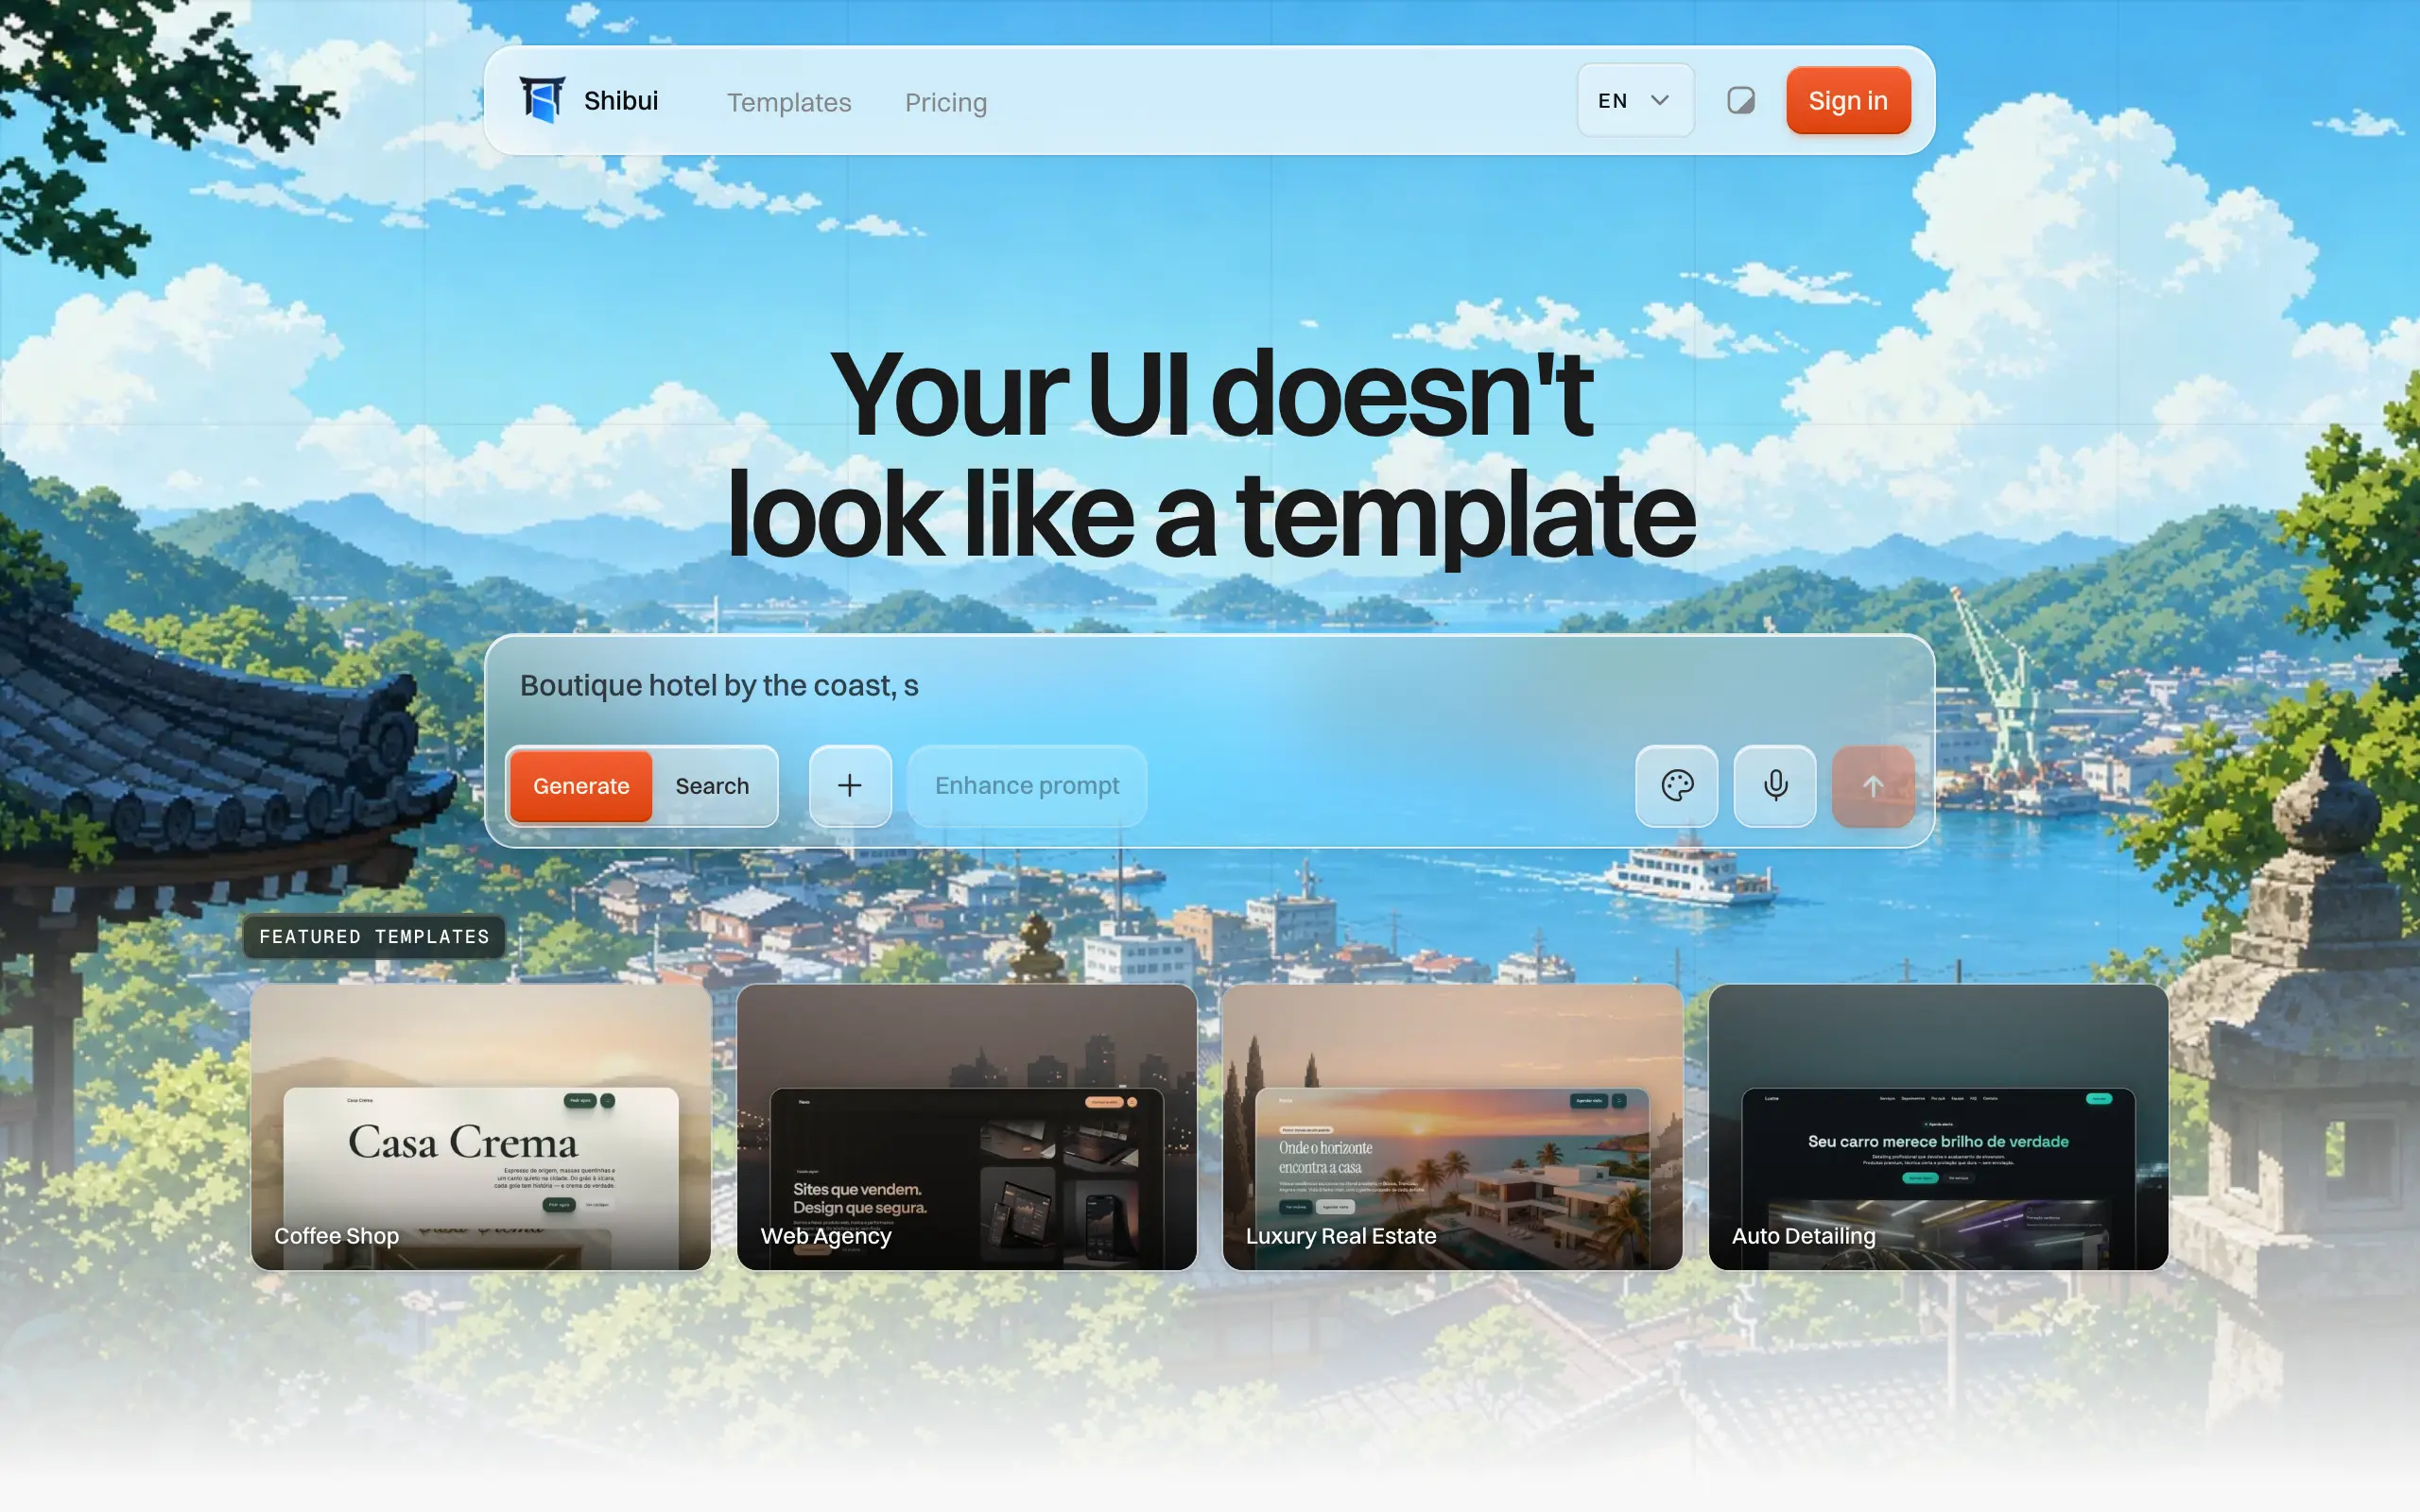
Shibui
AI website builder - describe your business, pick a niche template, edit by chatting, and publish instantly ✨
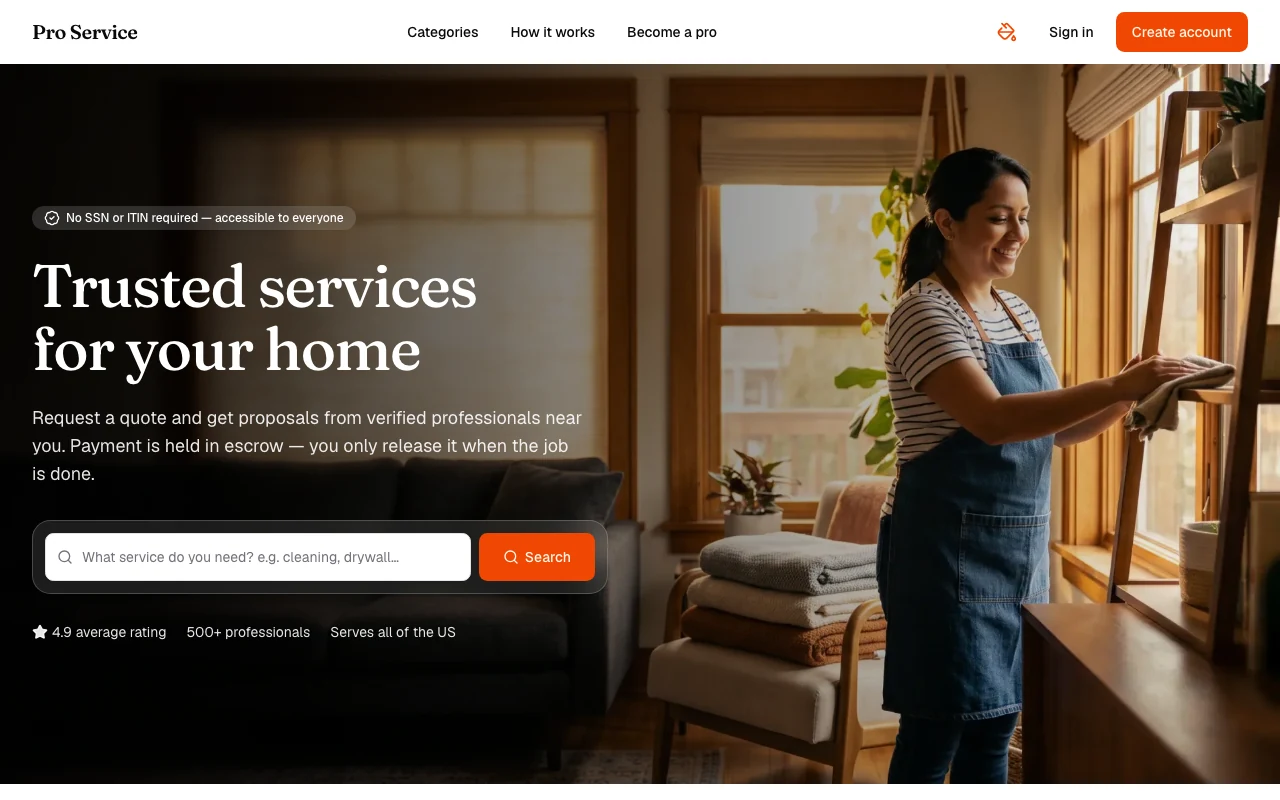
Pro Service
Find verified home service professionals, compare quotes, and pay securely through escrow - built for Brazilians across the US 🏠
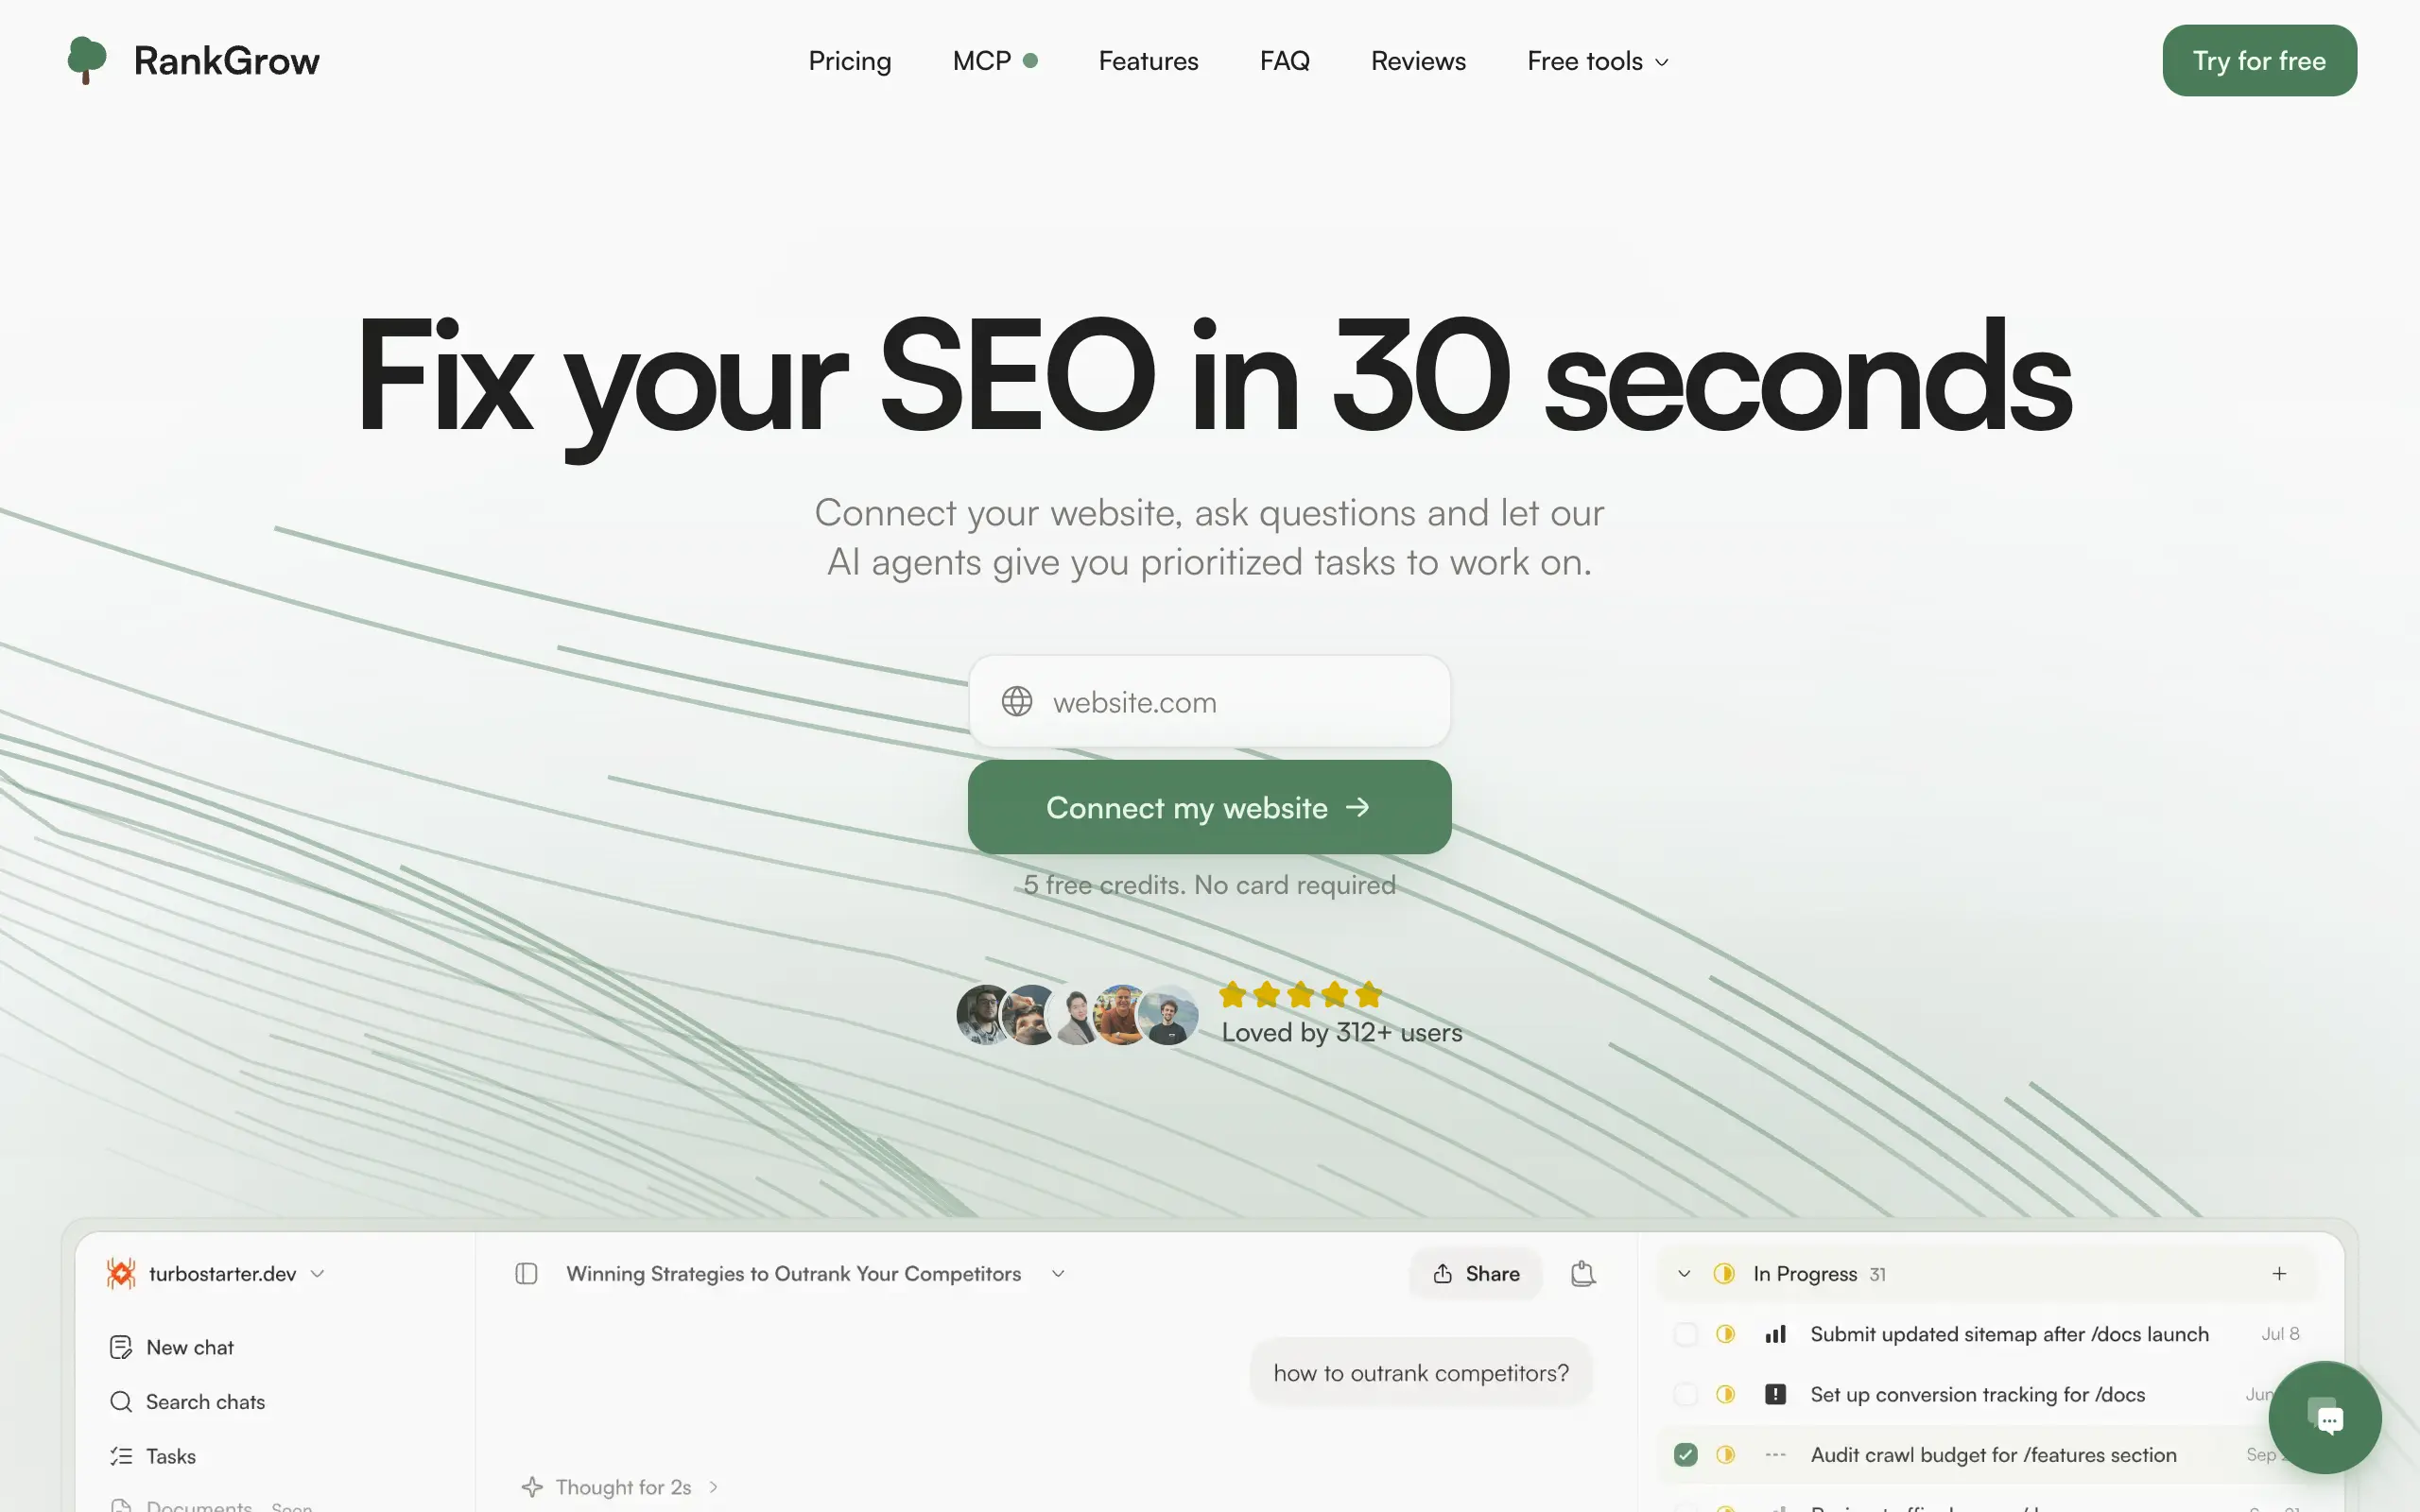
RankGrow
Fix your SEO with AI agents - connect Search Console, get prioritized tasks, and grow organic traffic 📈
SyncReads
Sync your favorite content for distraction-free reading, save time and replace multiple apps. Anytime, anywhere 🔄
Socialcrawl
Get clean, structured data from 21 platforms like TikTok, Instagram, and YouTube with a single request 📊
Statiko
Monitor any Telegram channel in real time - track posts, edits, deletions, and growth with AI recaps 📡
Shibui
AI website builder - describe your business, pick a niche template, edit by chatting, and publish instantly ✨
Pro Service
Find verified home service professionals, compare quotes, and pay securely through escrow - built for Brazilians across the US 🏠
RankGrow
Fix your SEO with AI agents - connect Search Console, get prioritized tasks, and grow organic traffic 📈
SyncReads
Sync your favorite content for distraction-free reading, save time and replace multiple apps. Anytime, anywhere 🔄
Socialcrawl
Get clean, structured data from 21 platforms like TikTok, Instagram, and YouTube with a single request 📊
Dotallio
Personalized AI apps that automate research, data extraction, and content creation without code 🤖
Talk to Santa
Enjoy a magical live video chat or receive a unique AI-generated video greeting from Santa Claus 🎅
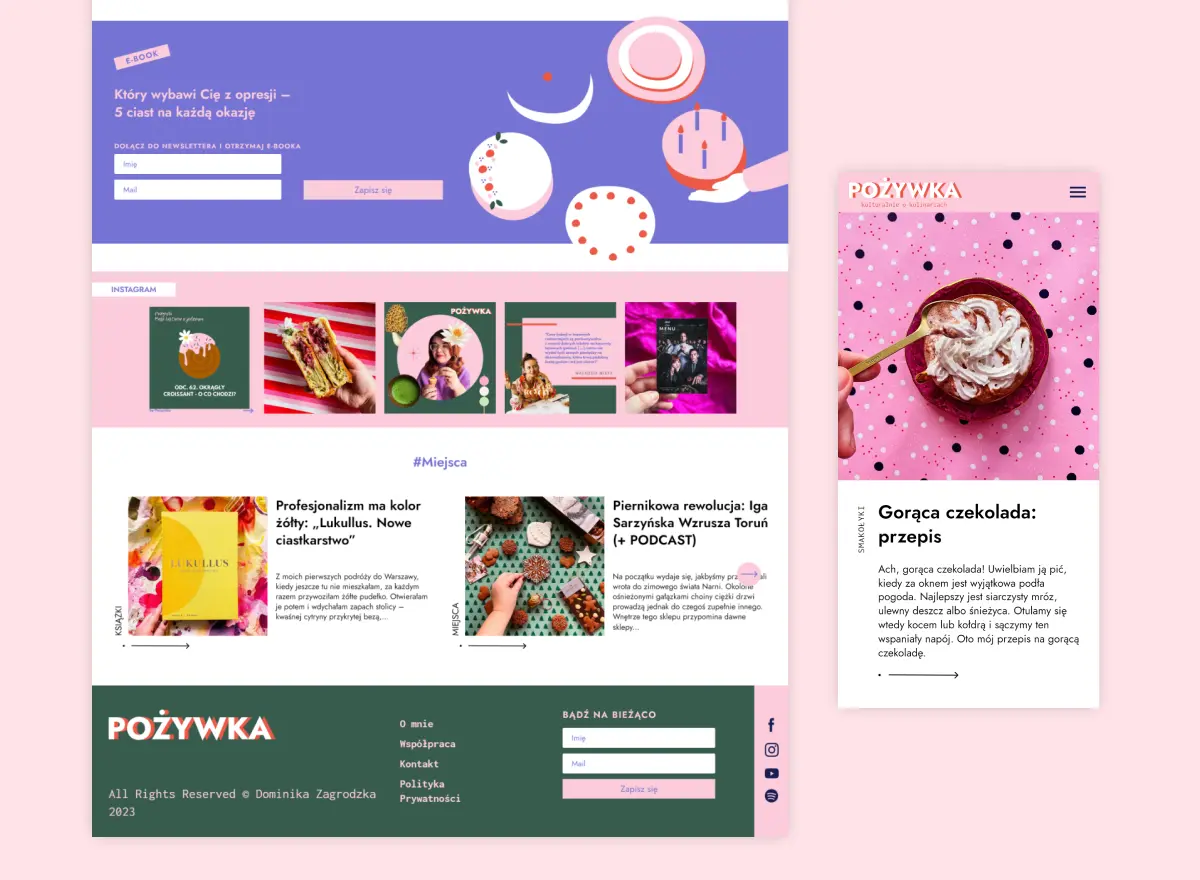
pozywka.pl
Scalable blog for food journalist, focused on performance and user experience 🌭
zagrodzki.me
Personal blog and portfolio of Bart Zagrodzki, where he shares his knowledge and work 💼
TurboStarter
Ship your startup everywhere. In minutes.
HTML to Markdown
Convert HTML to Markdown with ease, directly in your browser 📄
Dotallio
Personalized AI apps that automate research, data extraction, and content creation without code 🤖
Talk to Santa
Enjoy a magical live video chat or receive a unique AI-generated video greeting from Santa Claus 🎅
pozywka.pl
Scalable blog for food journalist, focused on performance and user experience 🌭
zagrodzki.me
Personal blog and portfolio of Bart Zagrodzki, where he shares his knowledge and work 💼
TurboStarter
Ship your startup everywhere. In minutes.
HTML to Markdown
Convert HTML to Markdown with ease, directly in your browser 📄
Omichat
Chat with 50+ AI models, including ChatGPT and Claude, in one place - switch models anytime without losing context 🤖
Claude Fast
Supercharge your Claude Code with 6x effective context window and specialized AI agents 🤖
EmojAI
AI-powered emoji picker with smart, context-aware suggestions 🤖
Solohacker
Autonomous company launcher - AI agents work 24/7, escalate what matters, and you stay in control 🤖
BeRawi: Storytelling Coach
Practice storytelling daily with instant feedback to sound clearer, more engaging, and confident 🎤
Omichat
Chat with 50+ AI models, including ChatGPT and Claude, in one place - switch models anytime without losing context 🤖
Claude Fast
Supercharge your Claude Code with 6x effective context window and specialized AI agents 🤖
EmojAI
AI-powered emoji picker with smart, context-aware suggestions 🤖
Solohacker
Autonomous company launcher - AI agents work 24/7, escalate what matters, and you stay in control 🤖
BeRawi: Storytelling Coach
Practice storytelling daily with instant feedback to sound clearer, more engaging, and confident 🎤
Connect with like-minded people
Join our community to get feedback, support, and grow together with 1,000+ builders on board, let's ship it!
Join usShip your startup everywhere. In minutes.
Don't burn tokens on setup and start building features on day one.