SpecScout
Track upstream API and OpenAPI changes, flag breaking diffs, and send migration-ready alerts to small SaaS teams maintaining third-party integrations.
What is SpecScout?
SpecScout is a B2B SaaS product for API change monitoring. It tracks upstream APIs and OpenAPI specifications, identifies changes that could break an integration, and sends engineering teams alerts with practical migration guidance.
The problem is familiar to any small SaaS team that depends on third-party APIs. A payment provider changes a field, a CRM deprecates an endpoint, or a vendor updates its API documentation. The integration may keep working for a while—or fail suddenly in production. In either case, developers need to discover the change, determine its impact, and decide what to do.
SpecScout’s promise is to make that process less reactive. Rather than asking engineers to repeatedly check vendor documentation or learn about a breaking change from an outage, it would monitor selected API contracts and notify the team when a meaningful change appears.
The product sits at the intersection of:
- API monitoring
- OpenAPI and schema diffing
- Dependency and integration risk management
- Developer notifications and workflow automation
- Migration planning
The best initial version should not attempt to monitor every API in every possible way. It should do one thing exceptionally well: help small teams understand which upstream API changes matter, why they matter, and what to do next.
The problem SpecScout solves
Small SaaS companies often depend on external APIs for essential product functions. A company might use one provider for payments, another for authentication, and several more for email, analytics, shipping, accounting, or customer support.
Each integration creates an ongoing maintenance obligation. The SaaS team must keep its implementation compatible with the provider’s API, SDK, authentication rules, and operational behavior. That obligation does not end when the initial integration ships.
API changes are difficult to manage for several reasons:
- Change information is distributed. Vendors may publish updates through changelogs, documentation pages, release notes, email lists, dashboards, or support announcements.
- The impact is hard to judge. A change can be harmless to one integration and critical to another.
- Documentation changes do not always explain implementation impact. A developer may need to compare versions, inspect schemas, and locate every affected call site.
- Small teams have limited monitoring capacity. They may not have a dedicated platform or integrations team.
- Discovery often happens too late. A team may learn about a change after tests fail, a customer reports an issue, or an integration starts returning errors.
SpecScout can address the discovery and triage stages. It should not claim that every alert predicts a production incident or that every migration can be generated automatically. Instead, it can reduce the time between an upstream change becoming visible and a team understanding its likely effect.
That is a clear, credible value proposition: find relevant API changes earlier, filter out noise, and make the next engineering action easier.
Who should use API change monitoring?
SpecScout’s strongest early market is not every company that uses an API. It is teams with enough integrations to experience change-management pain, but not enough engineering capacity to build a custom monitoring system.
Small SaaS engineering teams
A small product team may own dozens of integration touchpoints without a dedicated developer relations or platform engineering function. The team needs a lightweight way to watch important dependencies and route actionable alerts to the right engineers.
For this audience, onboarding must be fast. A user should be able to add an OpenAPI document, provide a public specification URL, or configure another supported source without a lengthy consulting engagement.
Integration-heavy SaaS products
Some software products are built around connecting customer systems or external services. These companies may rely on APIs from CRMs, payment processors, communication platforms, cloud services, or industry-specific vendors.
A change in a high-value integration can affect onboarding, synchronization, billing, reporting, or other core workflows. These teams may value impact ranking and ownership assignment more than a generic list of schema differences.
Agencies and implementation partners
Agencies that maintain integrations for multiple clients have a portfolio-monitoring problem. They need to know which client projects depend on which APIs and where an upstream change may require work.
A multi-workspace design, client-level reporting, and reusable integration inventories could make SpecScout useful to these firms. This is a promising expansion segment, but the first version should avoid building agency-specific complexity before validating demand.
Developer platform and operations teams
Larger organizations may already have internal tools for API governance, dependency management, or observability. They may still be interested in an external change feed for third-party services, especially if their internal platform focuses on APIs they own rather than APIs they consume.
This segment is likely to require stronger controls, audit logs, single sign-on, custom retention, and procurement support. It is better suited to a later stage than an initial launch.
Likely buyer and user roles
The person paying may be a CTO, engineering manager, or technical founder. The daily user is more likely to be a backend engineer, integrations engineer, or developer responsible for a particular provider.
That distinction matters for product design:
- The buyer wants fewer surprises, less maintenance risk, and clear visibility across dependencies.
- The engineer wants accurate diffs, low-noise notifications, source evidence, and a useful path to remediation.
- The team lead wants ownership, status tracking, and a record of what was reviewed.
A strong product serves all three without turning a developer tool into a heavyweight governance platform.
Market opportunity and product gap
API infrastructure is mature, but managing changes in APIs a company consumes remains fragmented. Teams can find vendor changelogs, documentation, SDK release notes, and API testing tools. Those tools help with parts of the problem, but they do not necessarily provide one consistent workflow for tracking upstream contracts and assessing changes across vendors.
This is the opportunity for SpecScout: a focused third-party API change management layer for teams that do not want to build one themselves.
Existing approaches and their limitations
Teams currently tend to combine several methods:
- Subscribe to provider release notes and mailing lists.
- Check documentation pages manually.
- Pin SDK versions and upgrade when convenient.
- Run integration tests on a schedule.
- Monitor production errors and investigate after symptoms appear.
- Build internal scripts that compare selected schemas.
- Rely on engineers to remember which vendors matter.
Each method has value, but each leaves gaps. Release notes may be incomplete or difficult to route. Tests detect behavioral failures only when they exercise the affected path. SDK pinning can delay exposure to a change, but it does not provide visibility into what the provider has announced. Custom scripts may work for a few specifications but can become another system to maintain.
SpecScout should therefore complement—not claim to replace—automated tests, production monitoring, and vendor communications. Its differentiated job is to turn upstream contract changes into a prioritized engineering workflow.
Why OpenAPI is a practical starting point
OpenAPI provides a structured way to describe HTTP APIs. It can document paths, operations, parameters, request bodies, responses, and schemas. The official specification is available at OpenAPI Specification.
That structure creates an opportunity for reliable comparison. Instead of comparing two documentation pages as raw text, a tool can parse both descriptions and identify changes such as:
- A removed endpoint or operation
- A renamed or removed field
- A new required request property
- A changed type or enum
- A modified response shape
- A changed authentication requirement
- A deprecated operation
- A change to parameter location or required status
OpenAPI is not the whole market. Some vendors publish incomplete specifications, proprietary formats, or documentation without downloadable contracts. SpecScout should begin with sources it can analyze reliably and expand to other source types only when it can preserve accuracy and explain uncertainty.
A focused wedge beats broad monitoring claims
The product should initially position itself around OpenAPI change monitoring for third-party integrations. This focus is specific enough to communicate value and narrow enough to build a trustworthy engine.
From there, the product can explore additional inputs:
- OpenAPI documents hosted at stable URLs
- Uploaded specification files
- Git repositories containing API contracts
- Vendor changelog pages
- SDK release metadata
- Selected API documentation formats
Each additional source increases coverage but also adds parsing, reliability, and support costs. A deliberate expansion strategy protects product quality.
Core features for an API change monitoring product
A useful SpecScout product needs more than a diff algorithm. It needs a workflow that connects a detected change to a person who can evaluate it.
1. API source registration
Users should be able to add an API source with minimal setup. The initial onboarding flow could support a public URL, file upload, or repository connection.
Each source should record:
- Provider or API name
- Environment or API version, where relevant
- Source URL or repository location
- Check frequency
- Team owner
- Importance to the product
- Date and version of the last successful check
Make the source status visible. If a URL stops responding or its format changes, users need to know that monitoring has become stale.
2. Scheduled source checks
SpecScout should fetch supported sources on a configurable schedule and detect whether a meaningful update occurred. Users should be able to choose reasonable intervals without exposing unnecessary infrastructure complexity.
The system should handle common operational conditions:
- Temporary network failures
- Rate limits
- Redirects
- Authentication changes
- Invalid or incomplete documents
- Identical content with a new timestamp
- Reordered schema properties that do not change behavior
Do not create duplicate alerts for transient failures. Treat source health as a separate concern from API contract changes.
3. Semantic schema diffing
A raw text diff is not enough. It can report a large number of changes caused by formatting, property order, or generated metadata that has no behavioral impact.
SpecScout’s comparison engine should parse supported documents into a normalized representation and compare their meaning. It should explain the change in terms developers recognize, such as “operation removed” or “request property is now required.”
The comparison should preserve evidence. A user should be able to inspect the old and new definitions, not merely trust a summary generated by the system.
4. Breaking-change classification
The product should distinguish between likely breaking changes, potentially risky changes, and generally additive changes. Classification rules must be documented and conservative.
For example, removing a response field may break a consumer that depends on it. Adding an optional response property is often compatible, but adding a required request property can break existing clients. Real-world compatibility can depend on provider behavior, generated clients, validation rules, and how the consuming application is written.
The interface should communicate this uncertainty. Use labels such as likely breaking, potentially breaking, and informational rather than presenting every classification as an absolute guarantee.
5. Impact context and ownership
An API diff becomes more valuable when SpecScout knows which product area depends on the affected operation. Users could attach a source to an integration, service, repository, or internal owner.
A mature version might connect API operations to code references or client libraries. That capability should be treated as an enhancement, not a prerequisite for the first release. Even manual ownership and importance labels can make alerts more useful.
6. Migration-ready alerts
An alert should answer four practical questions:
- What changed?
- Why might it matter?
- Which API operation or schema is affected?
- What should the team inspect next?
A good notification might include a concise summary, severity, source version, relevant links, and a suggested review checklist. It should avoid pretending to generate a safe code migration when the product has not inspected the customer’s implementation.
7. Review and resolution workflow
Teams need to record what happened after an alert arrives. A small workflow can include:
- New
- Acknowledged
- Investigating
- Action required
- Accepted or not applicable
- Resolved
Users should be able to assign an owner, add a note, and preserve the final decision. This helps prevent the same change from being rediscovered repeatedly.
8. Notifications and integrations
Email is a sensible initial channel. Slack or Microsoft Teams notifications can follow once the alert model is stable. Webhooks and issue tracker integrations may be useful for customers who want changes routed into existing processes.
Notifications should support filtering by severity, source, and workspace. If every harmless update creates a channel message, teams will mute the integration. Alert quality is a core product feature, not a finishing detail.
Recommended MVP scope
A compelling minimum viable product can be smaller than the full vision. The goal is to validate whether teams will repeatedly monitor their most important upstream APIs and act on the resulting alerts.
A practical MVP could include:
- Workspace and user accounts
- Public OpenAPI URL registration
- File upload for OpenAPI documents
- Scheduled polling with visible source health
- Semantic comparison for a defined set of change types
- Breaking-risk classification with explanations
- Email alerts
- A review and resolution status
- A timeline of prior checks and changes
- Basic plan limits and billing
Delay features that require difficult assumptions or broad compatibility, including automatic code changes, extensive vendor-specific integrations, deep repository indexing, and enterprise governance.
Build trust before breadth
A smaller set of well-explained, reproducible alerts is more valuable than broad source coverage that generates false positives. Show the exact evidence behind each detected change and make it easy for users to report a misclassification.
Recommended technology stack
The best stack depends on team expertise, expected workload, and whether the product is optimized for a rapid MVP or a highly customized platform. For an early-stage SaaS, favor technologies that make authentication, billing, background jobs, and observability straightforward.
Frontend
A React-based application is a practical choice for a developer-focused dashboard. React has a mature ecosystem for building interactive interfaces, including change timelines, diff views, filters, and team workflows.
Use server-rendered or hybrid rendering where it benefits the marketing site and authenticated application. Keep the main product interface responsive and accessible; users may review alerts from a laptop, tablet, or mobile device.
Backend and API
Use a backend framework the founding team can operate confidently. TypeScript can provide shared types between the frontend and backend, while Go, Python, or another language may be a better fit if the team has stronger experience in that ecosystem.
The application should separate:
- User-facing API requests
- Source fetching
- Document parsing and normalization
- Diff and classification logic
- Notification delivery
- Billing and account lifecycle events
This separation allows expensive or unreliable source checks to run asynchronously instead of blocking dashboard requests.
Database and job processing
A relational database such as PostgreSQL is a strong default for users, workspaces, sources, checks, changes, assignments, and billing records. These objects have clear relationships, and teams will need queries for history, ownership, and account-level reporting.
Use a job queue or managed background task system for scheduled checks. Jobs should support retries, backoff, idempotency, and dead-letter handling. Do not rely on a web server process staying alive to perform recurring monitoring.
Store original source documents and normalized representations in a way that supports auditability and efficient comparison. Object storage may be appropriate for larger historical files, while the relational database stores metadata and references.
Parsing and diffing
Build the comparison engine as a separately testable module. A reliable process should:
- Fetch a source and retain the response metadata.
- Validate and parse the document.
- Normalize irrelevant differences.
- Compare the new representation with the last valid version.
- Classify changes using explicit rules.
- Save evidence and create an event only when appropriate.
The tool should distinguish parse failures from successful checks with no changes. Otherwise, a broken source can appear healthy simply because no diff was produced.
Authentication, billing, and product foundation
For a small team, using a proven SaaS starter can reduce the time spent on foundational features such as authentication, team accounts, billing, and deployment setup. TurboStarter is one option to evaluate when choosing a starting point.
A starter kit does not replace product-specific engineering. The API source model, comparison engine, notification logic, tenant isolation, and auditability still need careful implementation.
Observability and security
Instrument background jobs, source fetches, parsing failures, alert delivery, and billing events. Track operational metrics such as check completion, stale sources, retry rates, and notification failures. Avoid collecting customer API credentials unless they are necessary for a supported source; if credentials are added later, encrypt them and restrict access.
At minimum, design for:
- Tenant isolation at the data-access layer
- Secure secret storage
- Role-based access where appropriate
- Audit trails for meaningful account actions
- Rate limiting on user-facing endpoints
- Clear data retention and deletion behavior
- Protection against unsafe URL fetching
The last point is especially important if users can register arbitrary URLs. Server-side fetchers must be designed to reduce risks such as access to internal network resources, unsafe redirects, or unexpectedly large responses.
Monetization strategy
SpecScout has a natural SaaS pricing model because customers receive ongoing monitoring rather than a one-time report. Pricing should reflect the amount of value delivered and the cost of maintaining sources, history, and notifications.
Free or trial plan
A free plan can help developers test the product with one or two APIs. Keep limits clear. The purpose is to demonstrate alert quality, not to provide an unlimited monitoring service without a path to conversion.
A time-limited trial may be preferable if ongoing monitoring costs are significant or if the product needs users to experience multiple check cycles before its value is obvious.
Team subscription
A paid team plan could include more monitored APIs, longer history, additional users, collaboration features, and more notification channels. This is likely the most straightforward early monetization model for small SaaS teams.
Avoid pricing solely by user seats if the core value is monitoring sources. A simple combination of monitored APIs, workspace capabilities, and retention may align more closely with customer value.
Business and enterprise plans
Larger plans could add features such as:
- Single sign-on
- Advanced roles and permissions
- Longer event retention
- Audit exports
- Private or authenticated source support
- Custom notification routing
- Service-level commitments
- Dedicated support
These features should be introduced in response to validated buyer needs. Building enterprise controls too early can slow product learning.
Pricing research
Treat initial price points as hypotheses, not established market facts. Interview buyers about the cost of current workarounds, the impact of missed API changes, and who controls the budget. Test willingness to pay with real plan proposals rather than relying only on abstract survey questions.
Track more than conversion. Monitor activation, the number of sources added, alert review rates, trial-to-paid conversion, expansion, churn, and the frequency with which alerts are marked irrelevant.
Competitive advantage and positioning
SpecScout’s advantage should not rest on the claim that no other tool can compare API schemas. A durable positioning strategy is about serving a specific user and workflow better than a collection of general-purpose tools.
Proposed unique selling proposition
SpecScout helps small SaaS teams catch meaningful changes in the third-party APIs they depend on, understand the likely impact, and route the work to the right person.
That statement is stronger than “API monitoring made easy” because it identifies:
- The target user: small SaaS teams
- The monitored asset: third-party APIs
- The key outcome: actionable change awareness
- The workflow: interpretation and routing
Differentiation opportunities
| Product capability | Manual monitoring | Generic text diff | Production monitoring | SpecScout opportunity |
|---|---|---|---|---|
| Tracks upstream specifications | Limited | Possible | Usually no | Core capability |
| Identifies contract-level changes | Inconsistent | Often noisy | Symptom-based | Semantic diff |
| Explains likely engineering risk | Depends on engineer | Limited | After impact appears | Prioritized interpretation |
| Routes work to an owner | Manual | Rarely included | Incident workflows | Lightweight team workflow |
| Preserves review decisions | Scattered | Limited | Incident history | Change audit trail |
The rightmost column describes a product opportunity, not a guarantee that no competitor offers similar capabilities. Competitive research should verify current products, positioning, and customer reviews before finalizing a market claim.
Defensibility over time
The code for a diff engine alone may not create a lasting moat. Potential sources of differentiation include:
- A high-quality change classification system
- Low false-positive rates across real-world specifications
- A library of provider-specific normalization rules
- Strong workflow integrations
- Useful historical data and review outcomes
- A trusted user experience that shows evidence clearly
Customer feedback can improve classification, but the product should not silently use private customer data to train shared systems. Explain any data use and provide suitable controls.
Risks and how to mitigate them
False positives and alert fatigue
If harmless changes are labeled breaking, users will stop trusting notifications.
Mitigation: Show evidence, use confidence-aware severity labels, let users tune notifications, and measure how often alerts are dismissed or reclassified. Treat false-positive reporting as a product feedback loop.
False negatives
A specification may omit behavior that exists in production, or a change may be breaking only because of a customer’s implementation.
Mitigation: Be explicit about the scope of analysis. Describe findings as contract-based risk signals, not proof that an integration will or will not fail. Encourage teams to run their own tests.
Incomplete or unstable source coverage
Vendors may move documentation, block automated fetches, change formats, or publish specifications that do not match deployed behavior.
Mitigation: Show the time of the last successful check, report stale sources, retain source versions, and make source health visible. Expand formats only when they can be supported reliably.
Secure fetching of customer-provided URLs
A monitoring product that fetches arbitrary URLs creates security concerns.
Mitigation: Use strict network controls, block private and reserved address ranges, validate redirects, set response size and time limits, and isolate fetch workers. Review the design with security professionals before launch.
Vendor terms and access restrictions
Some providers may restrict automated access to documentation or require authenticated API access.
Mitigation: Review applicable terms, support approved source methods, respect rate limits, and provide clear guidance for customer-owned or licensed sources. Do not assume that every publicly accessible page may be crawled without restriction.
Customer trust and data handling
Teams may be reluctant to provide repository access, API credentials, or internal dependency details to a new vendor.
Mitigation: Start with public specifications and uploads where possible. Minimize data collection, document retention, support deletion, and explain access controls in plain language. Add deeper integrations only when the security posture can support them.
Unclear willingness to pay
Some developers may find the concept useful but rely on manual checks or existing alerts.
Mitigation: Validate the problem before building a broad platform. Ask potential customers to describe recent API-change incidents, current workflows, and the cost of maintaining them. Seek paid pilots or preorders as stronger evidence than general enthusiasm.
How to validate SpecScout before building the full product
A disciplined validation process can prevent investment in features customers do not need.
Interview the right users
Talk to technical founders, engineering managers, and engineers responsible for integrations at small SaaS companies. Ask about actual behavior rather than hypothetical interest:
- How many third-party APIs does the product depend on?
- How do they currently learn about vendor changes?
- What happened the last time an upstream change caused work?
- Who reviews provider release notes?
- Which changes are most difficult to detect?
- What tools or scripts already exist?
- What would make an alert trustworthy enough to act on?
Look for repeated examples of missed updates, manual effort, or expensive investigation. If the main concern is production outages rather than contract changes, the initial product positioning may need to shift.
Test alert quality with real specifications
Collect a small set of public or customer-approved API specifications and compare versions. Ask engineers to review the generated results. Measure whether the tool identifies changes correctly and whether the explanations help users decide what to do.
A useful early success criterion is not simply “the parser works.” It is that users can identify important changes quickly and understand why the alert was sent.
Run a concierge pilot
Before automating every source type, offer a small group of design partners a limited monitoring service. The team can initially handle some source setup and review edge cases manually, while still measuring whether customers return to the product and act on alerts.
Keep the pilot transparent. Do not imply that a manual process is a fully automated capability.
Validate a pricing hypothesis
Present clear plan options to prospective customers and ask them to choose what they would actually purchase. Follow up with a pilot offer. Learn whether the buyer prefers pricing by monitored APIs, workspaces, retention, or team size.
Actionable implementation steps
A realistic build plan should reduce product risk before adding platform breadth.
1. Define the first customer and use case
Choose a narrow initial segment, such as small SaaS teams that rely on public OpenAPI specifications for critical integrations. Write down the team size, user roles, current workaround, and trigger that makes the problem urgent.
2. Interview prospective users
Conduct structured interviews with engineers and technical buyers. Ask for recent examples and existing workflows. Record the language customers use to describe breaking changes, maintenance burden, and alert fatigue.
3. Select supported source formats
Start with one or two source paths, such as a public OpenAPI URL and a file upload. Define which document versions and features are supported. Communicate unsupported formats rather than silently producing incomplete results.
4. Build a trustworthy diff prototype
Create a parser, normalized representation, and a first set of change rules. Test against versioned specifications and deliberately include formatting changes, missing fields, and malformed inputs. Store enough evidence for a user to verify every finding.
5. Add source health and history
Implement scheduled checks, retries, last-success timestamps, and a change timeline. Make failures visible. A monitoring tool that cannot distinguish “no changes” from “could not check” will undermine user trust.
6. Add useful alerts and review states
Start with email notifications and a small set of severity levels. Let users acknowledge, assign, and resolve changes. Avoid sending every detection to every team member by default.
7. Run a design-partner pilot
Invite a small number of teams to monitor APIs they genuinely depend on. Review alert accuracy, source failures, activation, and repeat usage. Ask users which alerts changed what they did—not merely whether they liked the interface.
8. Refine pricing and expand carefully
Test a simple subscription model, then expand sources and integrations based on repeated customer requests. Prioritize additions that improve the core workflow over features that only make the product appear broader.
The long-term product vision
SpecScout can begin as a focused OpenAPI change monitor and gradually become a broader third-party API dependency intelligence platform. Over time, it could help a team answer:
- Which external APIs are critical to our product?
- What changed since the last review?
- Which services own the affected integrations?
- Which changes are likely to require code work?
- What is the status of each review?
- Which monitored sources have become stale?
The opportunity is not to replace engineering judgment. It is to give engineers a reliable signal, preserve the evidence, and reduce the time spent searching across vendor documentation and internal conversations.
If SpecScout remains disciplined about accuracy, transparent about uncertainty, and focused on the needs of small SaaS teams, it can occupy a valuable space between manual release-note monitoring and heavyweight API governance. Start with a narrow source set, earn trust through high-quality alerts, and expand only when real usage demonstrates where the next layer of value lies.
More 🏢 B2B Application SaaS ideas
Discover more innovative b2b application SaaS ideas that are trending in 2026. Each idea is AI-generated with market validation and growth potential to help you find your next profitable venture faster than competitors.
Your competitors are building with TurboStarter
Below are some of the SaaS ideas that have been generated and built with our starter kit.
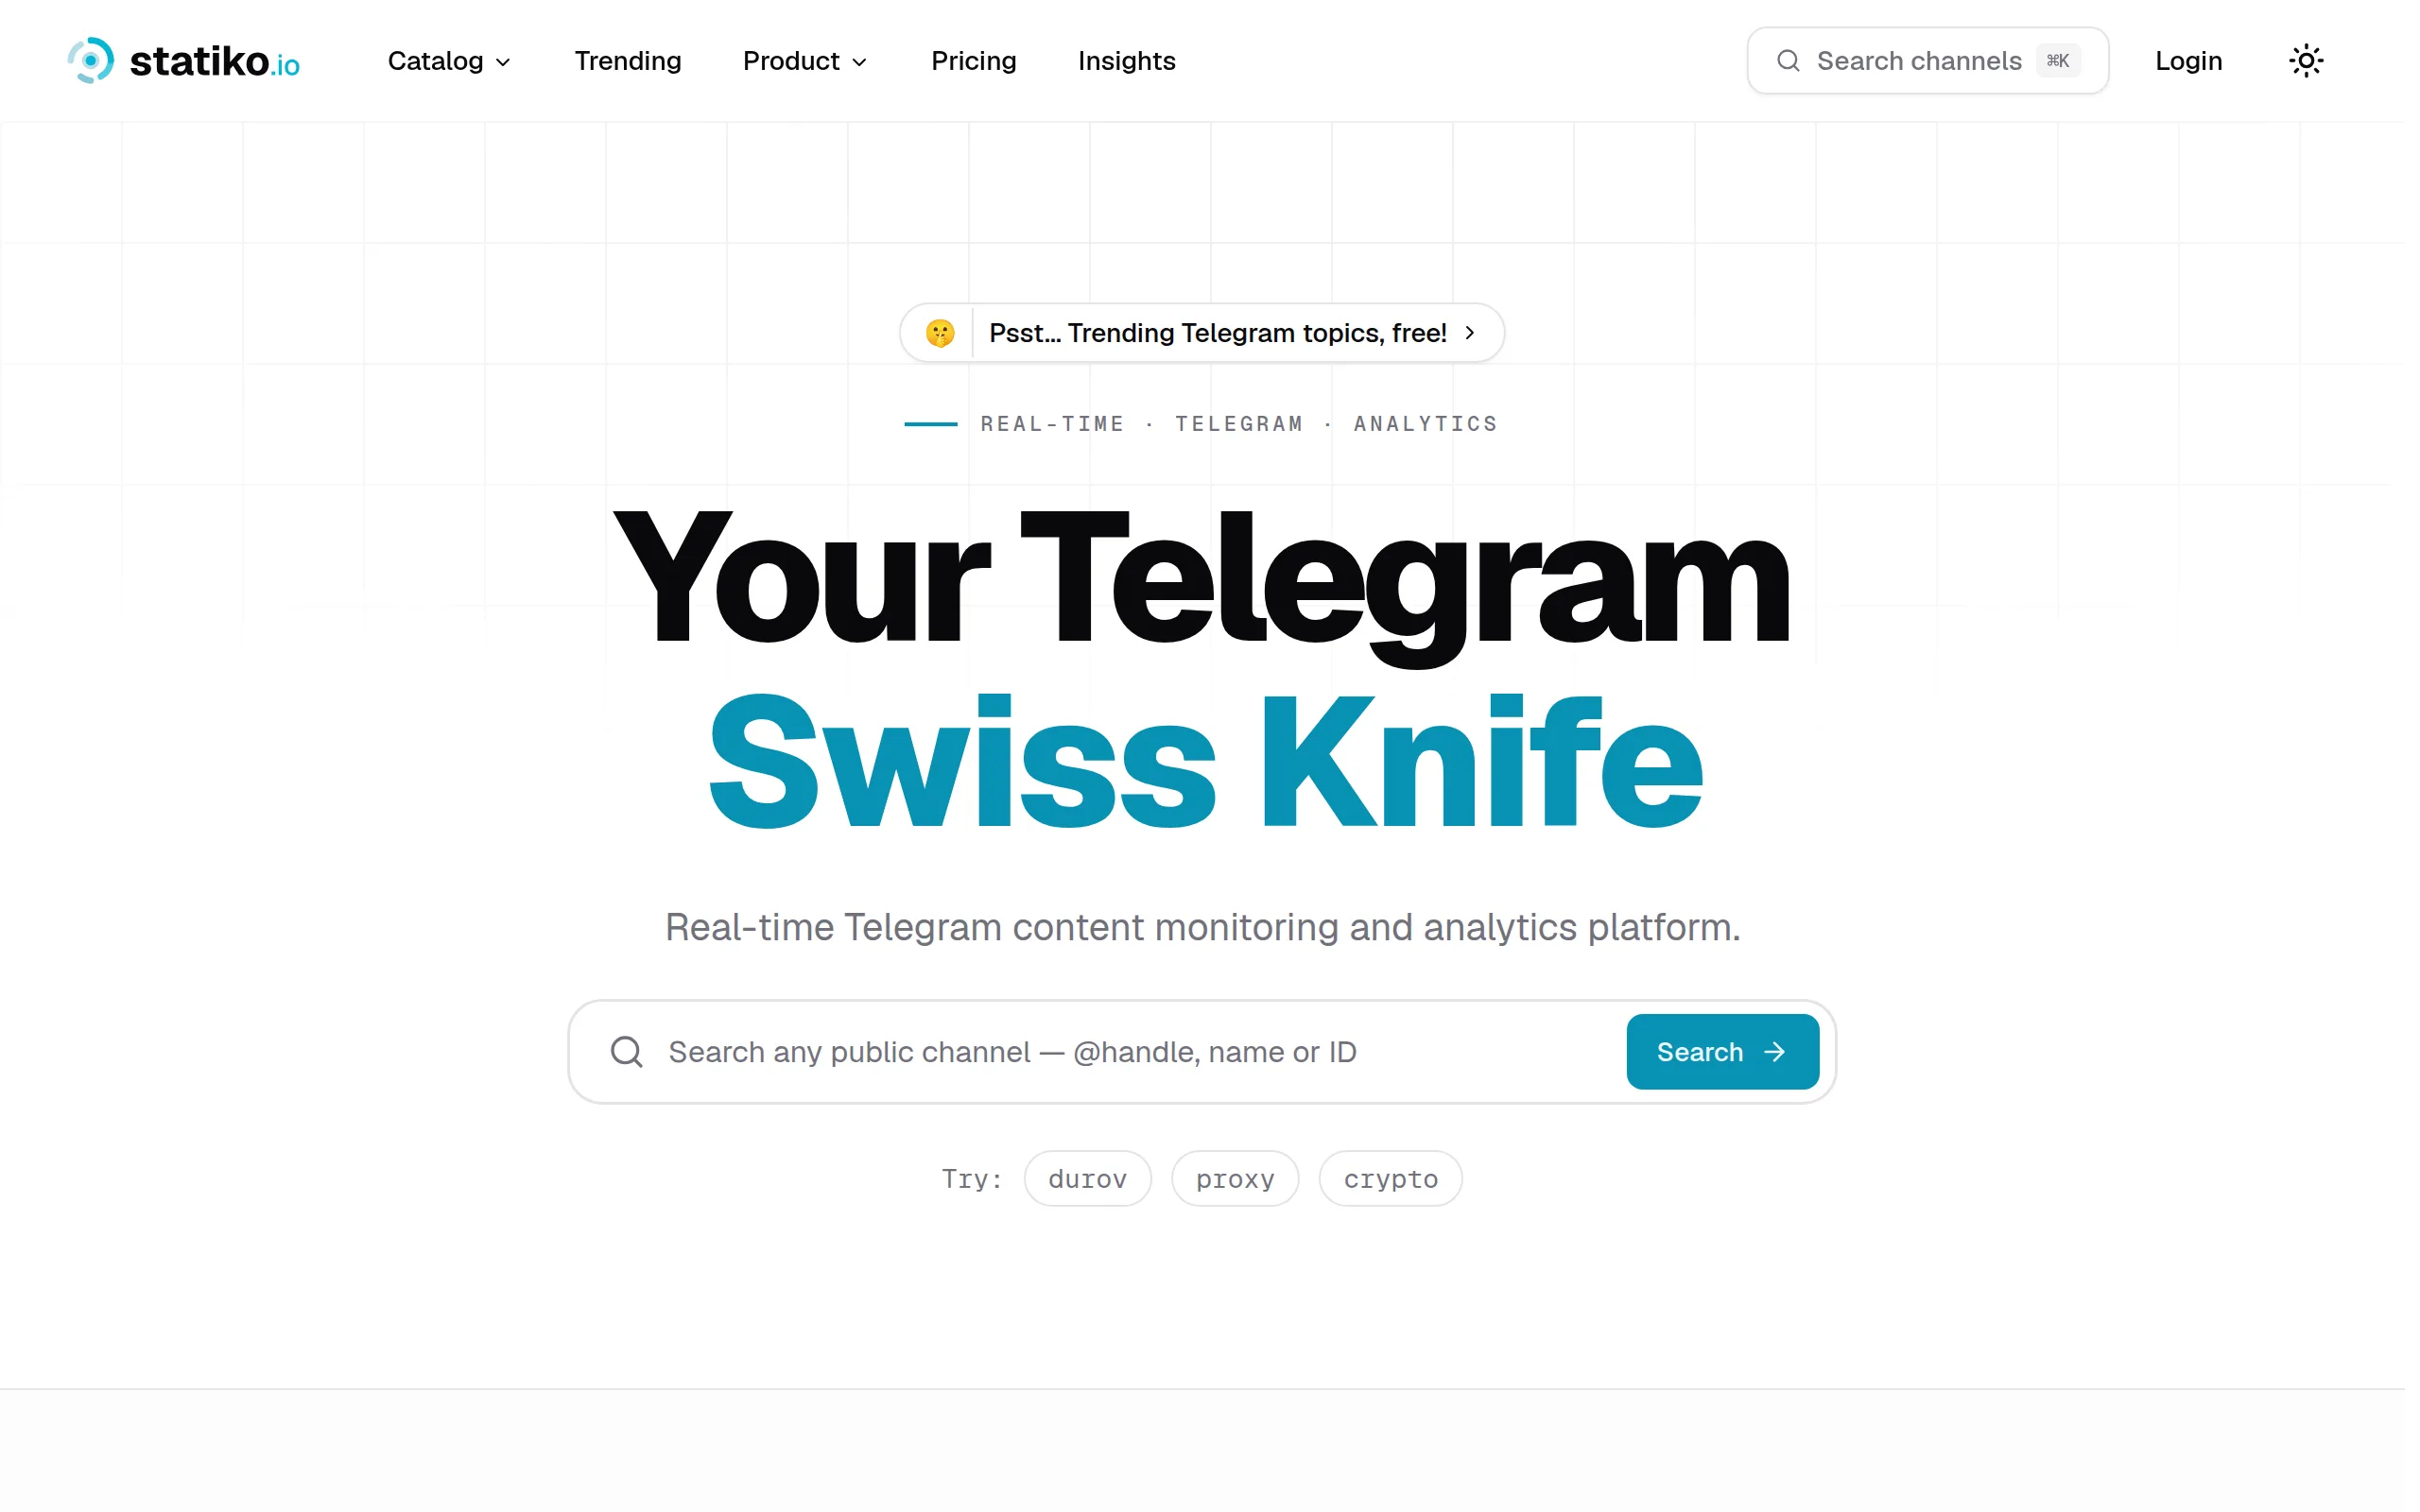
Statiko
Monitor any Telegram channel in real time - track posts, edits, deletions, and growth with AI recaps 📡
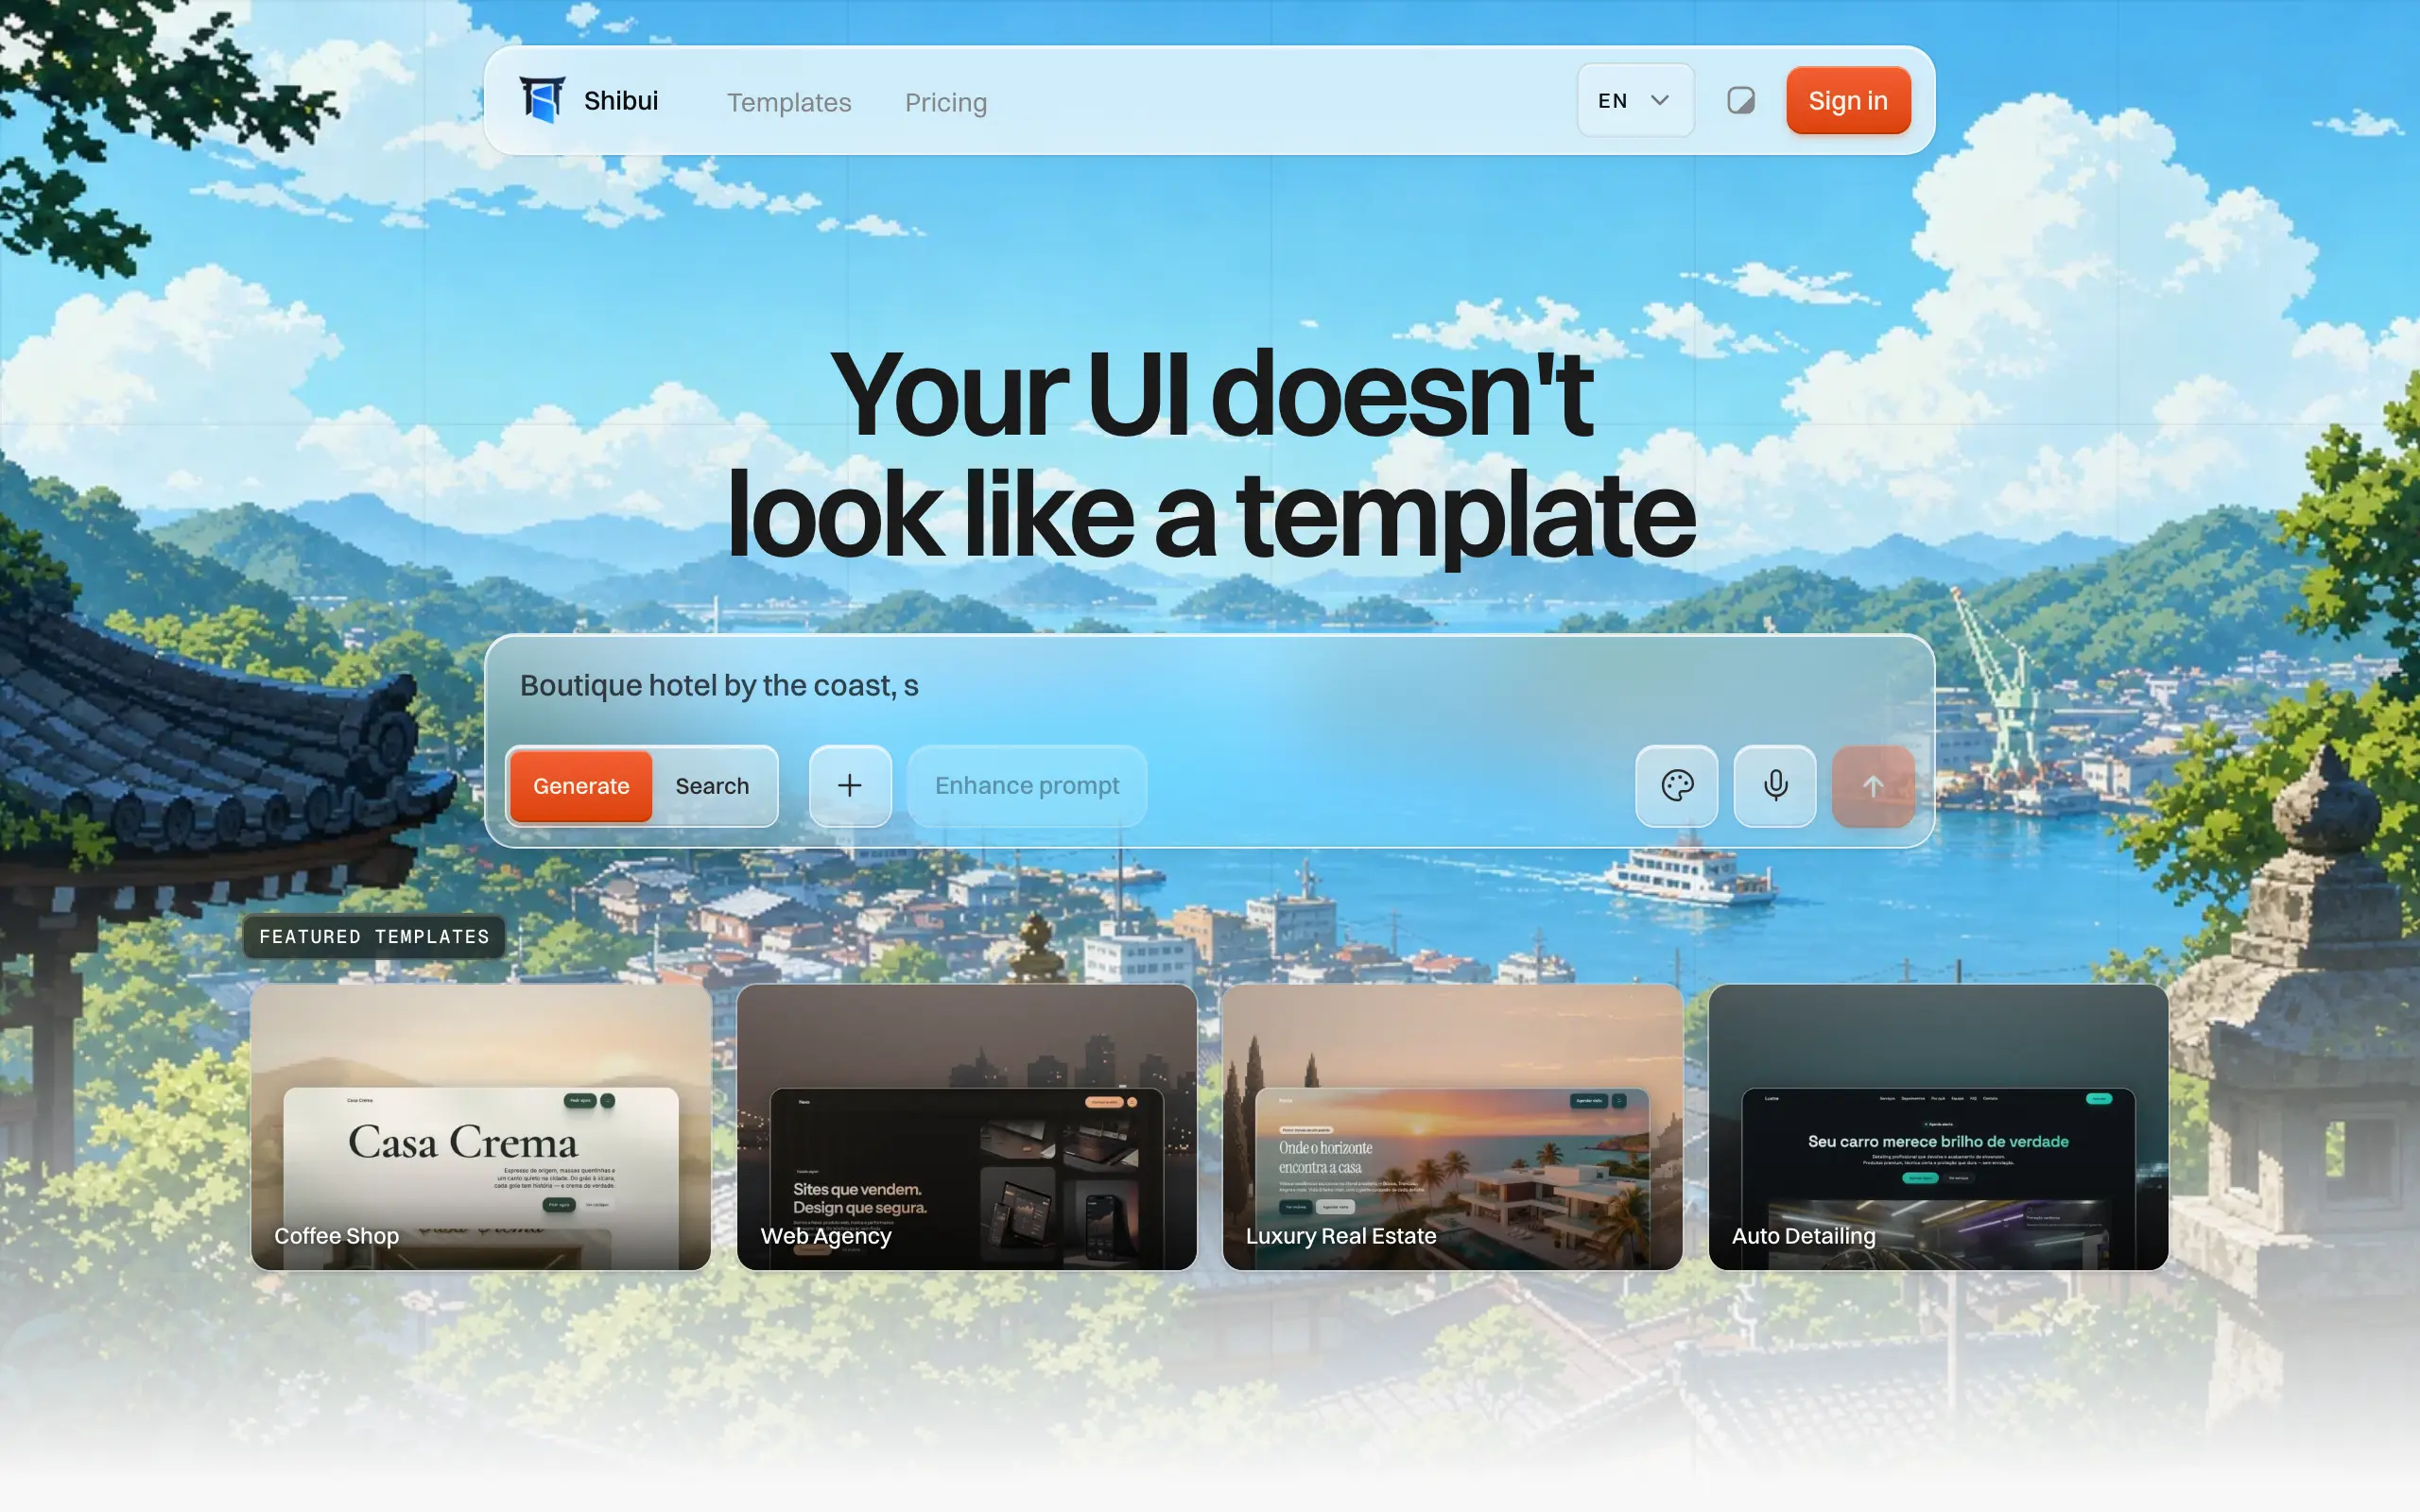
Shibui
AI website builder - describe your business, pick a niche template, edit by chatting, and publish instantly ✨
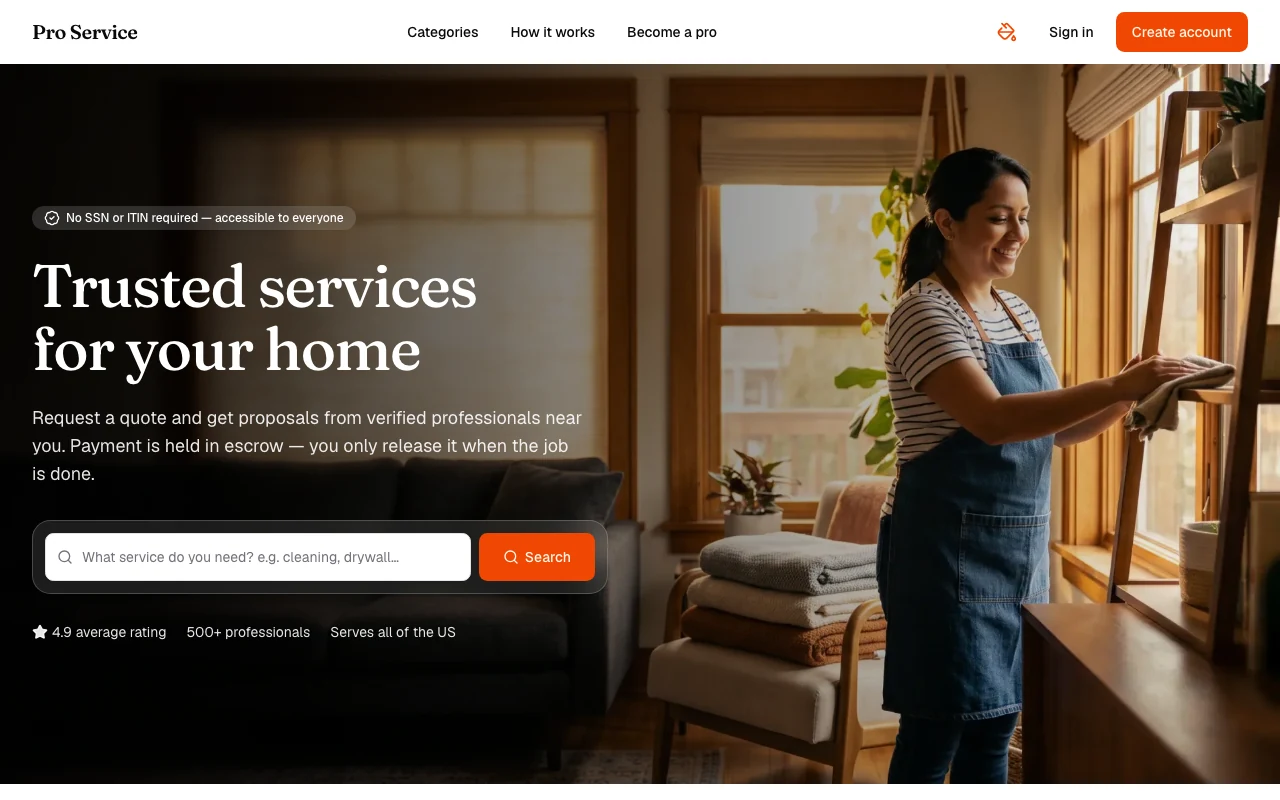
Pro Service
Find verified home service professionals, compare quotes, and pay securely through escrow - built for Brazilians across the US 🏠
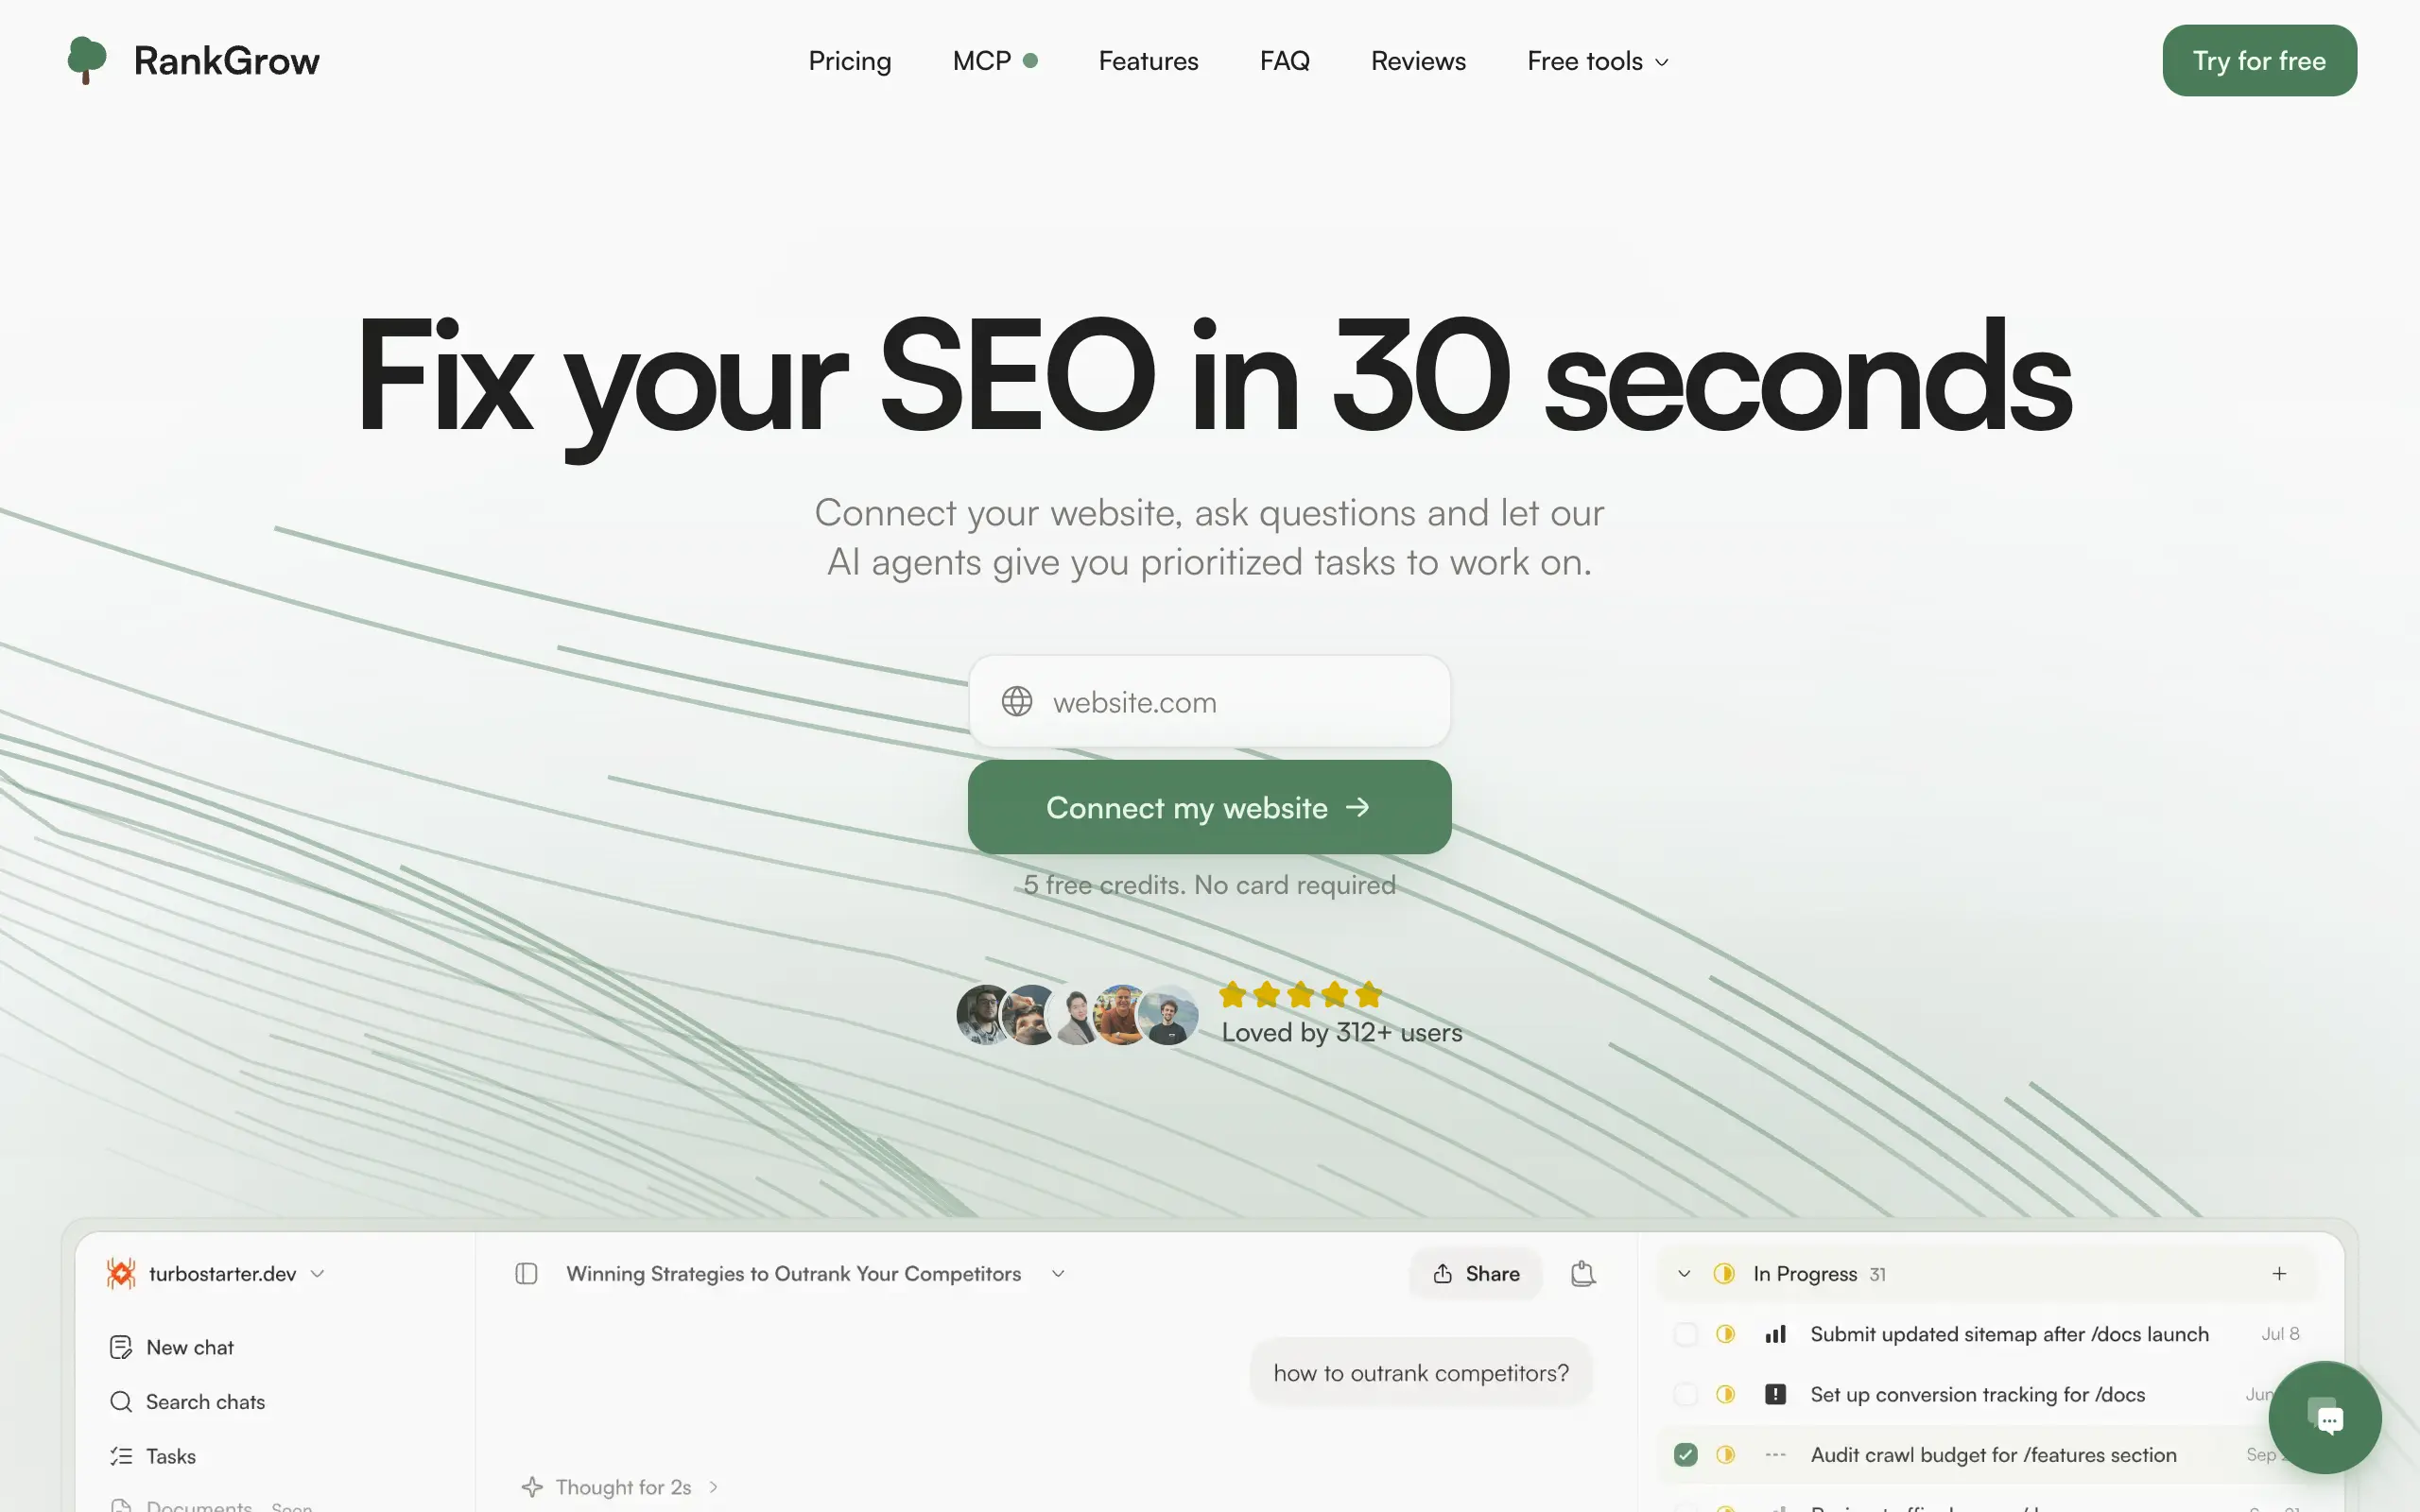
RankGrow
Fix your SEO with AI agents - connect Search Console, get prioritized tasks, and grow organic traffic 📈
SyncReads
Sync your favorite content for distraction-free reading, save time and replace multiple apps. Anytime, anywhere 🔄
Socialcrawl
Get clean, structured data from 21 platforms like TikTok, Instagram, and YouTube with a single request 📊
Statiko
Monitor any Telegram channel in real time - track posts, edits, deletions, and growth with AI recaps 📡
Shibui
AI website builder - describe your business, pick a niche template, edit by chatting, and publish instantly ✨
Pro Service
Find verified home service professionals, compare quotes, and pay securely through escrow - built for Brazilians across the US 🏠
RankGrow
Fix your SEO with AI agents - connect Search Console, get prioritized tasks, and grow organic traffic 📈
SyncReads
Sync your favorite content for distraction-free reading, save time and replace multiple apps. Anytime, anywhere 🔄
Socialcrawl
Get clean, structured data from 21 platforms like TikTok, Instagram, and YouTube with a single request 📊
Dotallio
Personalized AI apps that automate research, data extraction, and content creation without code 🤖
Talk to Santa
Enjoy a magical live video chat or receive a unique AI-generated video greeting from Santa Claus 🎅
pozywka.pl
Scalable blog for food journalist, focused on performance and user experience 🌭
zagrodzki.me
Personal blog and portfolio of Bart Zagrodzki, where he shares his knowledge and work 💼
TurboStarter
Ship your startup everywhere. In minutes.
HTML to Markdown
Convert HTML to Markdown with ease, directly in your browser 📄
Dotallio
Personalized AI apps that automate research, data extraction, and content creation without code 🤖
Talk to Santa
Enjoy a magical live video chat or receive a unique AI-generated video greeting from Santa Claus 🎅
pozywka.pl
Scalable blog for food journalist, focused on performance and user experience 🌭
zagrodzki.me
Personal blog and portfolio of Bart Zagrodzki, where he shares his knowledge and work 💼
TurboStarter
Ship your startup everywhere. In minutes.
HTML to Markdown
Convert HTML to Markdown with ease, directly in your browser 📄
Omichat
Chat with 50+ AI models, including ChatGPT and Claude, in one place - switch models anytime without losing context 🤖
Claude Fast
Supercharge your Claude Code with 6x effective context window and specialized AI agents 🤖
EmojAI
AI-powered emoji picker with smart, context-aware suggestions 🤖
Solohacker
Autonomous company launcher - AI agents work 24/7, escalate what matters, and you stay in control 🤖
BeRawi: Storytelling Coach
Practice storytelling daily with instant feedback to sound clearer, more engaging, and confident 🎤
Omichat
Chat with 50+ AI models, including ChatGPT and Claude, in one place - switch models anytime without losing context 🤖
Claude Fast
Supercharge your Claude Code with 6x effective context window and specialized AI agents 🤖
EmojAI
AI-powered emoji picker with smart, context-aware suggestions 🤖
Solohacker
Autonomous company launcher - AI agents work 24/7, escalate what matters, and you stay in control 🤖
BeRawi: Storytelling Coach
Practice storytelling daily with instant feedback to sound clearer, more engaging, and confident 🎤
Connect with like-minded people
Join our community to get feedback, support, and grow together with 1,000+ builders on board, let's ship it!
Join usShip your startup everywhere. In minutes.
Don't burn tokens on setup and start building features on day one.