For the complete documentation index, see llms.txt. Prefer markdown by appending.mdto documentation URLs or sendingAccept: text/markdown.
Overview
Better Auth authentication with ready-to-use sign-in flows, customer sessions, account recovery, social providers, and server-side access checks.
Edge Kit connects authentication to your interface, customer sessions, database, and email. You get ready-to-use sign-in flows and server-side session checks that you can reuse across your product's features.
The included authentication supports:
- Email and password accounts, verification, and password recovery.
- Social sign-in with Google, GitHub, and Cloudflare integrations.
- Anonymous access for experiences customers can try before registering.
- Account settings for profile details, linked accounts, and active sessions.
- Bot protection and rate limiting for protected authentication actions.
Use the included screens as they are or compose them into your own onboarding and account experience.
The kit uses Better Auth with the Drizzle SQLite adapter. Auth requests reach its handler through src/routes/api/auth/$.ts at /api/auth/*.
Why Better Auth?
One of the core principles of TurboStarter is to do things as simple as possible, and to make everything as performant as possible.
Better Auth provides an excellent developer experience with minimal configuration while keeping enterprise-grade security. Its framework-agnostic approach and focus on performance make it the perfect choice for TurboStarter.
Recently, Better Auth announced an incorporation of Auth.js (28k+ stars on GitHub), making it even more powerful and flexible.
Methods visibility
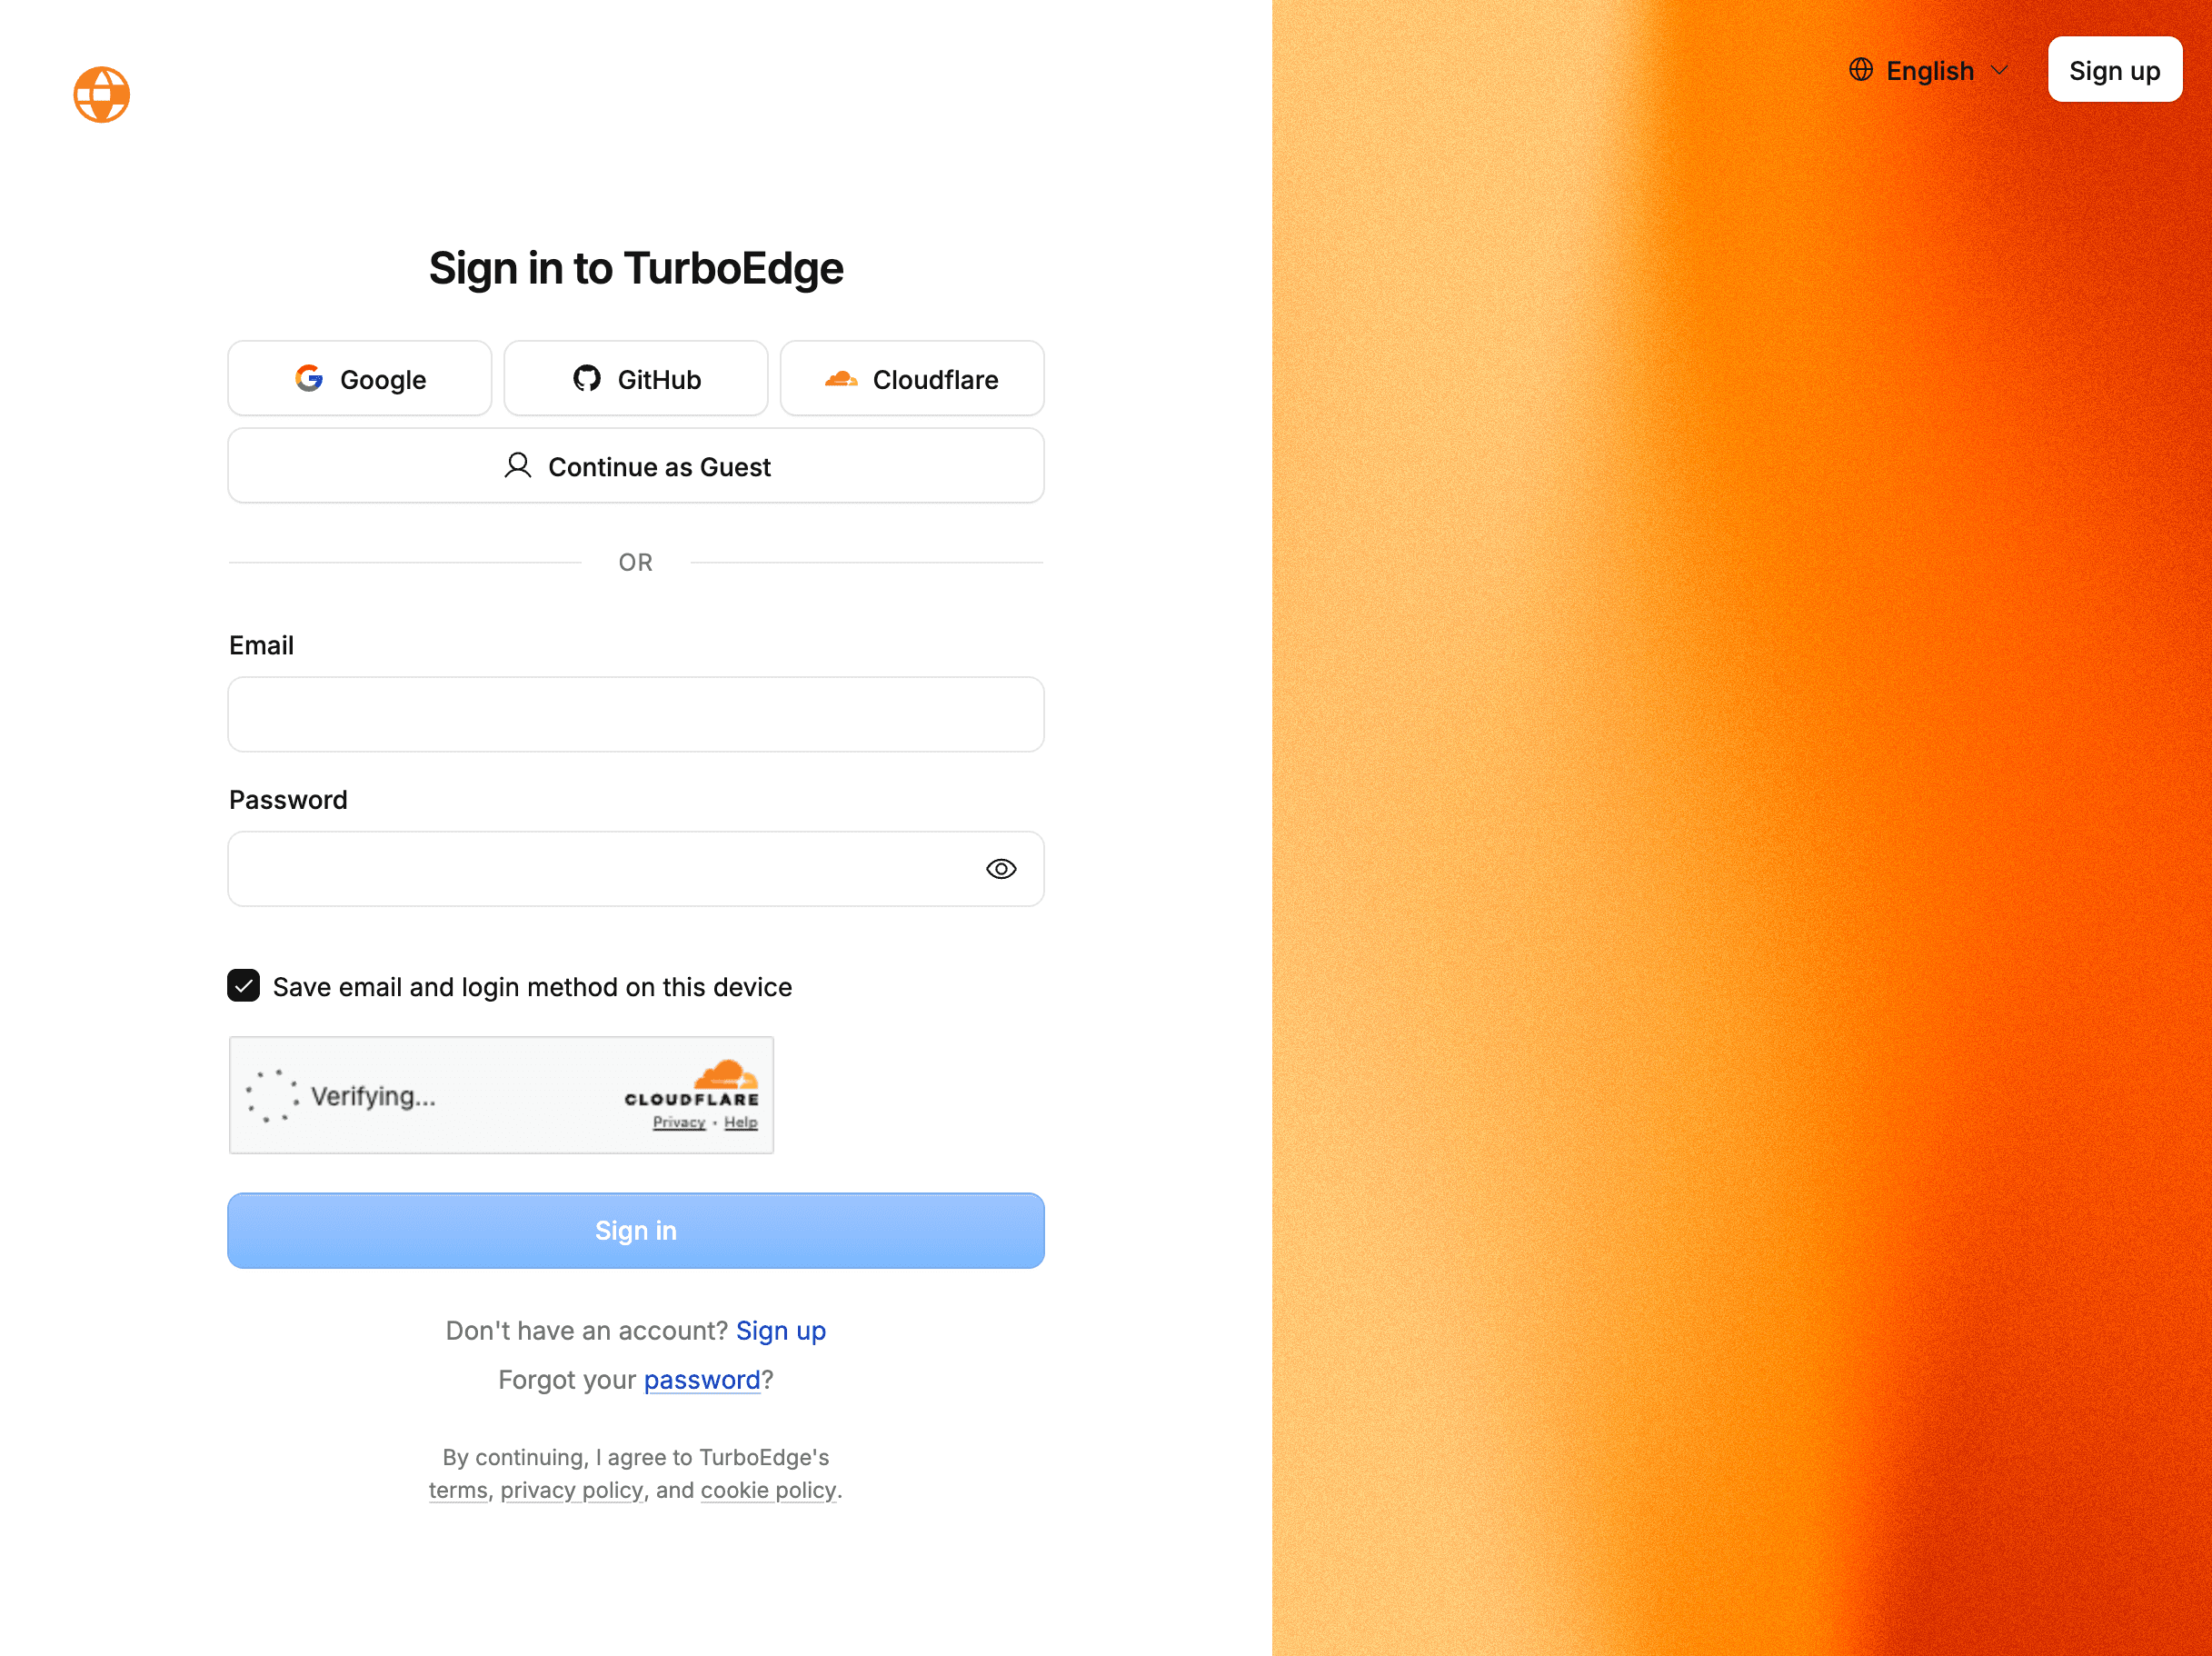
Use auth configuration to show password sign-in, anonymous access, or the Google, GitHub, and Cloudflare buttons.
Method availability
The password and anonymous switches control the visible interface. Server configuration controls which methods accept requests. When removing a method from your product, update both its server configuration and its sign-in controls.
Anonymous sign-in creates a valid session, allowing a customer to try a feature before registering. For actions that need a registered or verified customer, apply that policy on the server. Paid features can also use plan authorization.
Data protection
The included session checks protect private server functions and HTTP endpoints, giving your feature a trusted customer identity for database queries and file access.
Apply those checks to the operation that reads or changes data, alongside any ownership or plan policy. Dashboard redirects help navigation; the server checks protect the underlying operation. Protected calls covers the pattern for your own features.
Bot protection and rate limiting
The auth server installs Better Auth's Turnstile captcha plugin. Auth forms send the widget response for protected auth actions. The contact form uses a separate enforceCaptcha middleware, remember that captcha alone does not authenticate a user.
Authentication rate limiting is connected to Cloudflare's rate-limit binding. Adjust its window and allowance together with the authentication policy when adapting the product. Workers rate limiting semantics explains the scope of those limits.
Replace the Turnstile test keys before production. Keep key setup in auth configuration and Wrangler configuration.
Configuration
Choose sign-in methods in src/config/auth.ts. Toggle password and anonymous auth, and select which OAuth providers are shown.
OAuth providers
Connect Google, GitHub, and Cloudflare sign-in, register the correct callback URLs, and understand trusted account linking in Edge Kit.
Sessions
Customer identity and sessions in Edge Kit, including server checks, anonymous access, session revocation, and private application data.
Account management
Ready-to-use profile and security settings, with email changes, password recovery, linked accounts, sessions, and subscription-aware account deletion.
How is this guide?
Last updated on